MD2 generator
Generate an MD2 hash for any string input.
MD2 generator is a free tool that creates a fixed-length MD2 hash from text for legacy compatibility and data integrity comparisons.
What information does an MD2 digest contain?
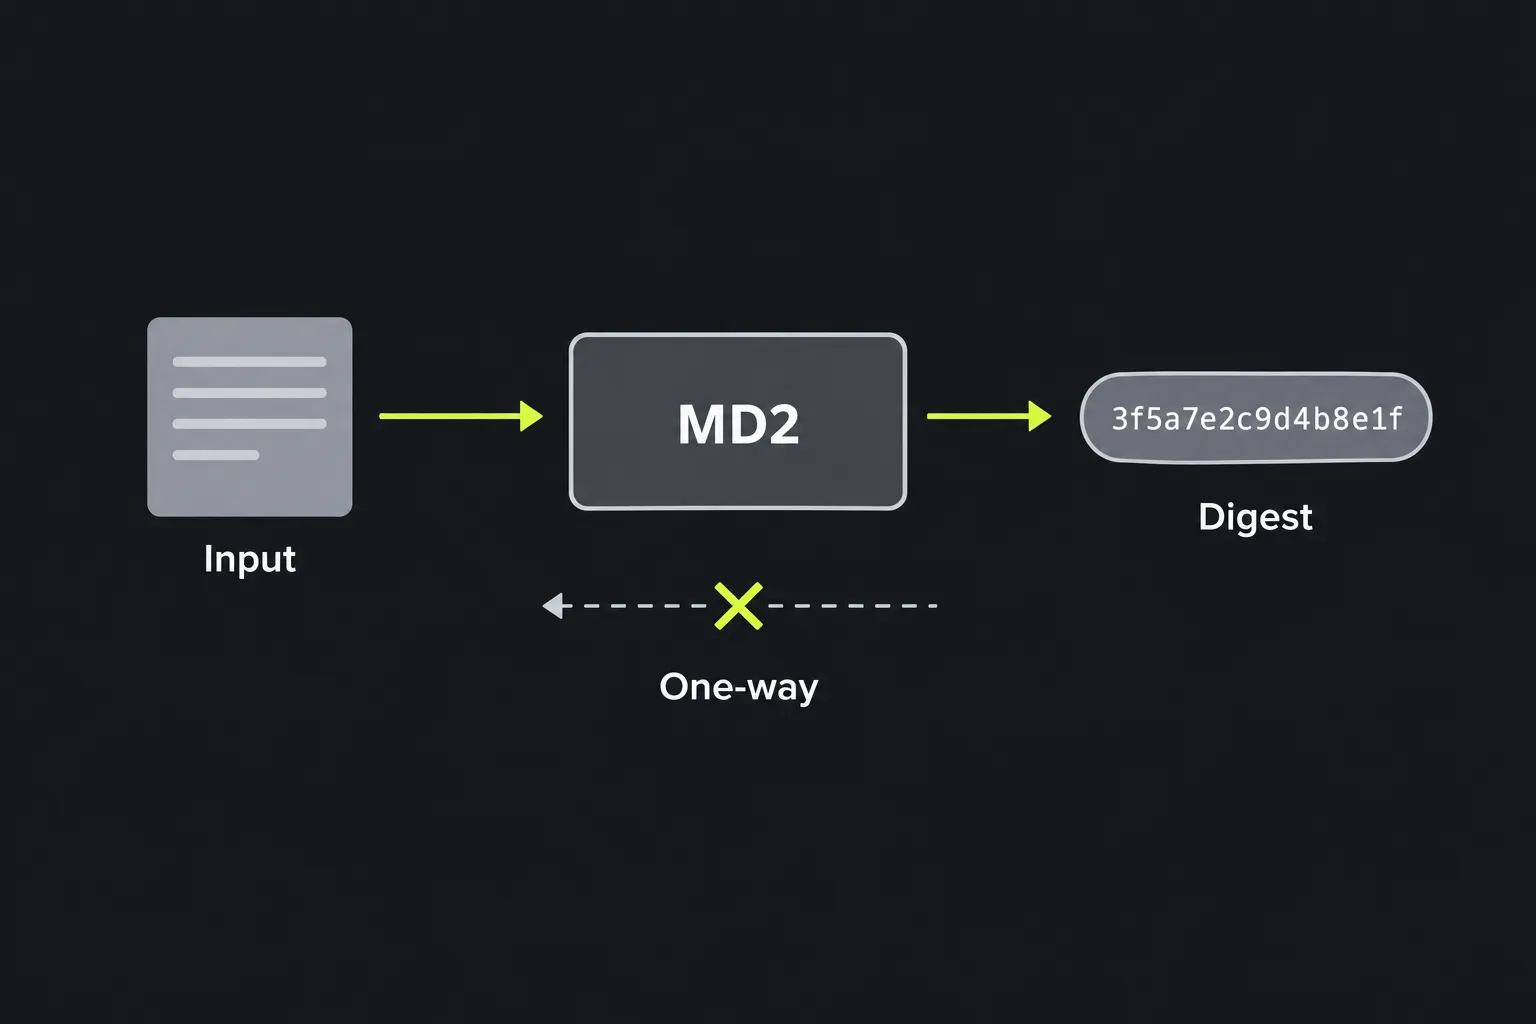
An MD2 digest is a 128-bit fingerprint of input data, commonly written as 32 hexadecimal characters. MD2 converts any amount of data into a fixed-length result. MD2 is one-way, so the digest does not contain a copy of the original input and cannot be decoded like encrypted data.
Ronald Rivest designed MD2 in 1989 for computers that processed data efficiently on 8-bit machines. The algorithm was later documented in RFC 1319 in 1992. Its design predates MD4 and MD5 and uses an internal checksum plus repeated transformations over 16-byte blocks.
MD2 is now cryptographically broken and deprecated. Researchers have found practical weaknesses in its collision resistance, meaning an attacker can construct different inputs that produce the same digest. RFC 6149 moved MD2 to Historic status and advises against using it where collision resistance is required.
What happens to text submitted to this tool?
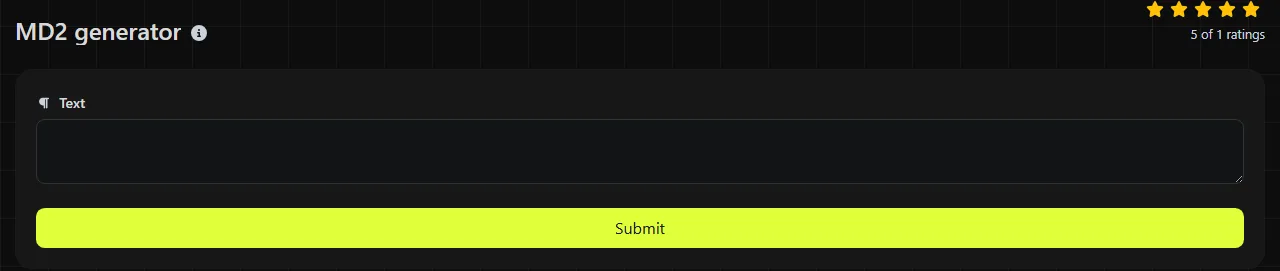
The text is sent to the server over HTTPS, where the server calculates the hash and returns it in the MD2 Hash field. This MD2 generator does not store the input. Because processing occurs on the server, avoid submitting passwords, private keys, access tokens, or other sensitive values.
This MD2 generator operates on the bytes of its string input, so every detail of the input can affect the result.
- Spaces, line breaks, tabs, and punctuation are part of the input.
- Uppercase and lowercase letters produce different digests.
- Numbers entered in a text field are hashed as character data, not as mathematical values.
- Accented and non-Latin characters depend on their byte encoding. Two visually identical characters can have different Unicode representations and therefore different hashes.
- Very long input still produces a 128-bit result. The algorithm itself also defines a digest for empty input.
When comparing an MD2 result from this tool with another program, use the same text encoding and line endings. A final newline copied from a terminal or text editor is a common source of mismatches.
Standard MD2 test vectors
Published test vectors provide a practical way to confirm that an implementation is calculating MD2 rather than another 128-bit algorithm. These two examples come from the standard MD2 test data.
- An empty input produces 8350e5a3e24c153df2275c9f80692773.
- The input "abc" produces da853b0d3f88d99b30283a69e6ded6bb.
Each output has 32 hexadecimal characters because two hexadecimal characters represent each of the 16 digest bytes. That length alone does not identify the algorithm. MD4 and MD5 digests are also commonly displayed as 32 hexadecimal characters.
Is it possible to recover the original input from an MD2 digest?
No, an MD2 hash cannot be decrypted or directly reversed because hashing does not use a reversible encryption key. If an MD2 digest is exposed, someone can still guess likely inputs, hash each guess, and compare the results. Short identifiers, common words, and predictable codes may therefore be discovered through dictionary or brute-force searches.
A matching guess does not necessarily prove that the guessed input was the original one. MD2 has known collision weaknesses, and multiple inputs can share a digest. The 128-bit output also represents far fewer possible values than the set of all possible inputs.
Should MD2 be selected for a new application?
No, MD2 should not be selected for a new security-sensitive application. Instead of MD2, use a currently accepted cryptographic hash for integrity checks and a dedicated password-hashing function such as Argon2id, bcrypt, scrypt, or PBKDF2 for password storage.
MD2 still has limited legitimate uses when an existing format or system specifically requires it.
- Comparing a legacy software package with an MD2 checksum published for that exact package.
- Identifying duplicate records in an old database whose stored fingerprint column uses MD2.
- Reproducing values required by archival software, obsolete protocols, or historical test suites.
- Investigating an old certificate or signature format that identifies MD2 as its digest algorithm.
An MD2 checksum can detect accidental changes if the expected value comes from a trusted source. It cannot safely protect against an attacker who can alter both the data and the published checksum. If a legacy record expects another 32-character digest, confirm the algorithm before using the MD4 generator or MD5 generator, since equal output length does not make those formats interchangeable.
Frequently asked questions
Does MD2 use a secret key?
No. Standard MD2 is an unkeyed hash, so anyone with the same input can calculate the same digest. If a system needs message authentication, use HMAC with an approved hash rather than treating an MD2 digest as proof of who created the data.
Why does an old certificate say md2WithRSAEncryption?
That identifier means the certificate's RSA signature was created using an MD2 digest. Many current certificate validators reject or disable MD2-based signatures because the hash no longer provides adequate collision resistance. Accessing such a certificate for archival analysis may require isolated legacy tooling rather than weakening normal browser or system security settings.
Is every 32-character hexadecimal hash an MD2 hash?
No. MD2, MD4, and MD5 all produce 128-bit digests that are commonly shown as 32 hexadecimal characters, and other hashes may be truncated to the same length. You need metadata, documentation, or a known test input to identify a result as MD2 reliably.
Can MD2 prove that a downloaded file is safe?
No. A matching MD2 value only shows that the calculated digest matches the expected digest, subject to MD2's known weaknesses. An MD2 result does not scan for malware, verify the publisher, or establish that the expected checksum itself came from a trustworthy source.
Before relying on an MD2 result, preserve the exact input bytes, record that MD2 was the required algorithm, and treat the digest as a legacy compatibility value rather than a current security control.
Similar tools
Popular tools
Create a WhatsApp chat link from a phone number, with an optional prefilled message.