SSL Lookup
Look up details about an SSL certificate.
SSL Lookup is a free tool that retrieves certificate issuer details, validity dates, and signature type for a host and port.
Which host and port should I enter?
Enter the DNS hostname of the service and the network port on which it accepts TLS connections. For a typical HTTPS website, that means a host such as www.example.com and port 443. Enter the hostname without a page path, query parameters, spaces, or login credentials.
- For https://store.example.com/checkout, enter store.example.com and port 443.
- For an HTTPS administration service on port 8443, enter its hostname and port 8443.
- For mail using implicit TLS, port 465 for SMTP or port 993 for IMAP may be appropriate, depending on the server configuration.
Internationalized domain names can be represented in ASCII Punycode, such as xn--mnich-kva.example. A port must be a valid integer from 1 through 65535. Empty input does not identify a service to check, while punctuation such as slashes or question marks belongs to a URL rather than a hostname.
The submitted input travels to the server over HTTPS, where the work is performed. It is not stored. Because the lookup runs on the server, its network path and DNS view can differ from those of your browser or office network.
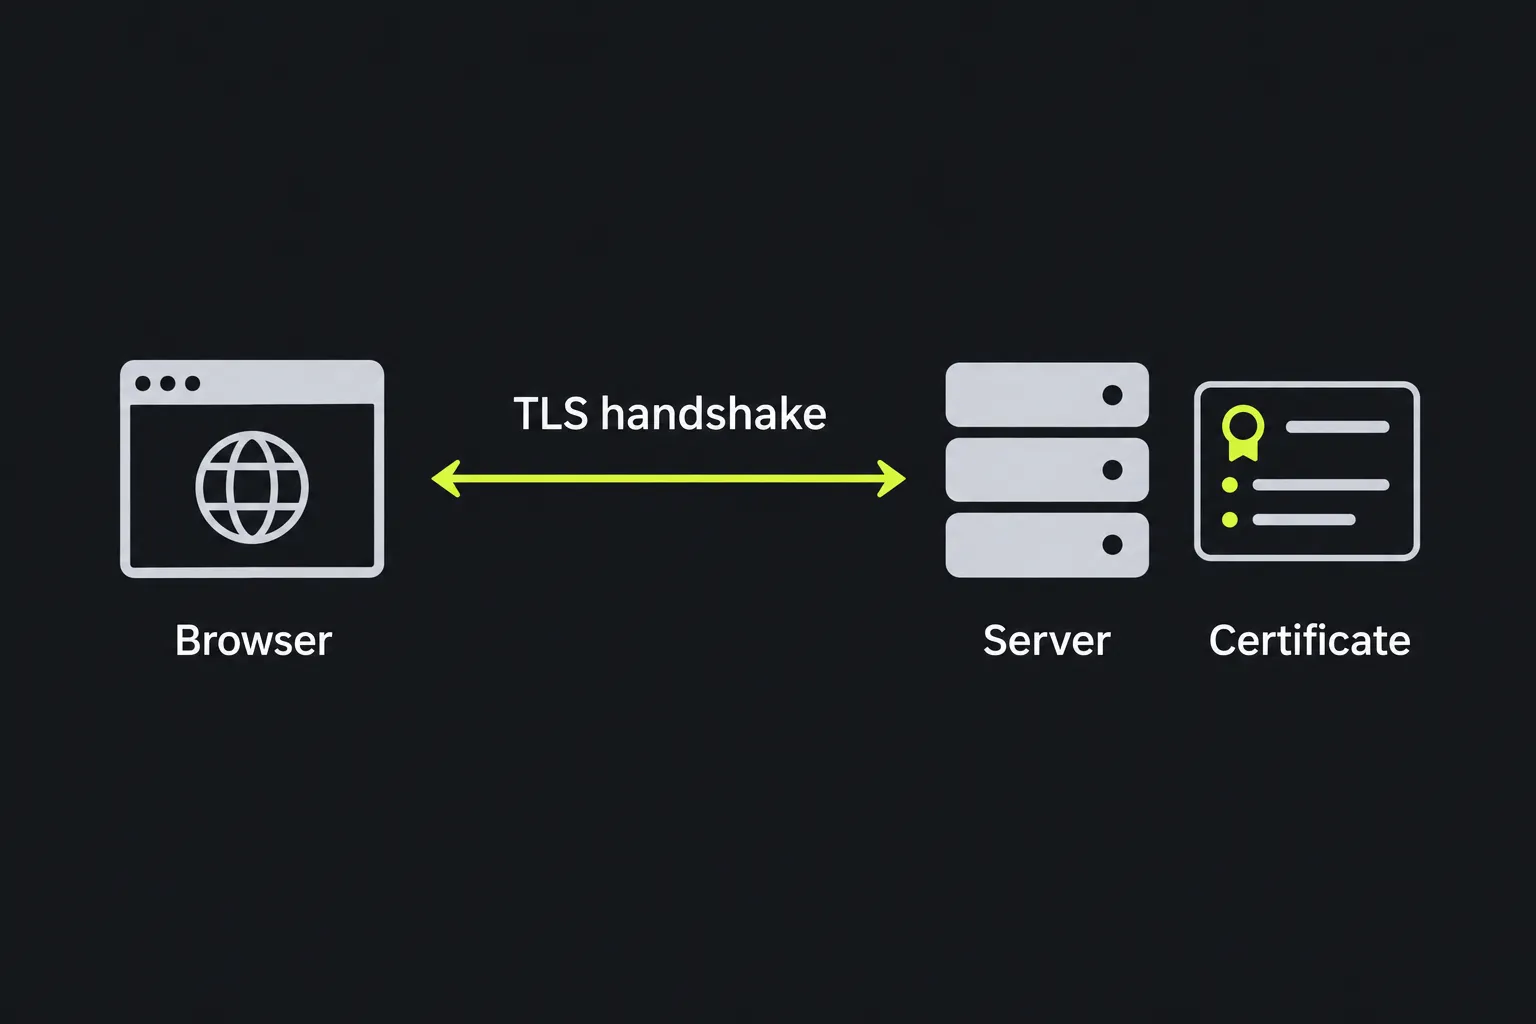
How does a TLS client evaluate a certificate?
A TLS service presents an X.509 certificate during connection setup so the client can evaluate the service name, validity period, issuer, and certificate path. The term SSL remains common in tool names, although modern web and mail connections generally use TLS.
A certificate contains a public key and is signed by a certificate authority. The CA signature allows a client to verify the issuer and detect unauthorized changes while validating the certificate path. The signature by itself does not prove that the site belongs to a particular person or company.
For service identity, current clients compare the requested DNS name with dNSName entries in the certificate's subjectAltName extension, as specified by RFC 9525. They no longer use the certificate Common Name for this purpose. SSL Lookup does not return subjectAltName entries or the complete chain, so its result cannot by itself confirm hostname matching or full browser trust.
Result fields and their practical meaning
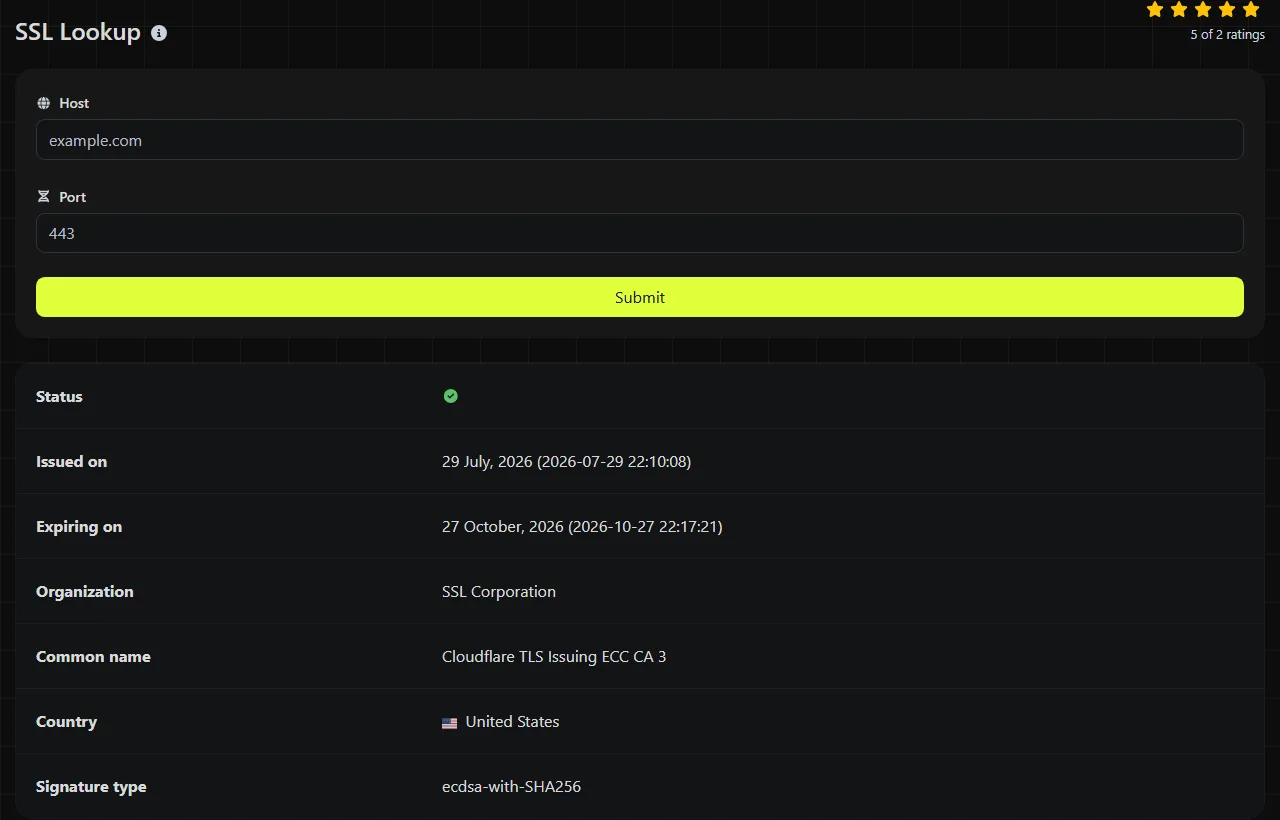
The result separates issuer information from validity boundaries and signature information. In this tool, Organization and Common name describe the issuing certificate authority, not the website's subject.
| Result field | What it tells you |
|---|---|
| Organization | The organization associated with the issuing CA. It does not establish who owns or operates the website. |
| Common name | The issuer certificate's Common Name, such as a CA product or intermediate name. Do not compare this value with the hostname. |
| Issued on | The X.509 notBefore boundary, which is the earliest time the certificate is valid. It is not guaranteed to be the exact purchase, creation, or issuance time. |
| Expiring on | The X.509 notAfter boundary. Clients should reject the certificate after this time. |
| Signature type | The algorithm used by the issuer to sign the certificate. This identifies the certificate signature method, not the negotiated encryption cipher for a visitor's connection. |
For example, a result showing Google Trust Services under Organization and WE1 under Common name identifies issuer information. It does not mean the checked website is named WE1. To verify the website name, you would need to inspect the certificate's subjectAltName entries with a client or browser that displays them.
Why can two visitors receive different certificates?
Two visitors can receive different certificates when their connections reach different servers, CDN edges, or cached DNS destinations. This commonly appears after renewal or a hosting change.
If one load-balanced backend still has the previous certificate files, only requests routed to that backend may show the old dates. A service may also have the new files on disk but continue presenting the old certificate until its web server, proxy, or mail service is reloaded. CDNs can present certificates from edge nodes independently of the origin server.
DNS caching matters when certificate replacement coincides with a DNS or hosting change. A resolver with an older DNS answer may send a visitor to the former server, while another resolver reaches the new one. DNS caching does not normally explain an old certificate when the address and hosting path have not changed.
Can an SSL lookup diagnose website and email problems?
An SSL lookup can narrow down certificate-related failures, but it cannot diagnose every website or email problem. Use the returned fields as evidence alongside browser errors, server logs, DNS records, and direct tests from the affected network.
- Certificate expiration warning. Compare the current time with Expiring on. If the date has passed, the server is presenting an expired certificate, even if a replacement exists elsewhere.
- Warning after a domain change. The displayed issuer fields cannot prove that the certificate covers the new hostname. Check subjectAltName entries separately, remembering that *.example.com covers shop.example.com but not checkout.shop.example.com.
- Mail delivery or connection failure. Implicit-TLS services can be checked through their TLS port. SMTP on ports 25 and 587 usually requires a protocol-level STARTTLS command before the certificate appears, which a generic TLS lookup may not perform.
If the hostname does not resolve at all, certificate details are unlikely to identify the cause because the service must first be reachable. IP Lookup can help confirm the address associated with an accessible host, while Whois Lookup can provide domain registration information. Neither replaces checking authoritative DNS records.
SSL lookup questions people often ask
Can a wrong computer clock cause a certificate warning?
Yes. A client clock set before the notBefore boundary can report that a certificate is not yet valid, while a clock set too far ahead can make it appear expired. Confirm the device's date, time, and time zone before replacing a certificate that appears valid elsewhere.
Can TLS run on a port other than 443?
Yes. Port 443 is the conventional HTTPS port, but private applications, control panels, APIs, and development services may use ports such as 8443. Enter the port where that specific service is configured to present its certificate.
How early should I replace a certificate before it expires?
Plan for enough time to issue, deploy, reload, and verify the replacement across every backend and edge service. Do not schedule the change for the final hours of the validity period. Record the old and new expiration dates during deployment so you can identify any server that still presents the previous certificate.
Similar tools
Popular tools
Create a WhatsApp chat link from a phone number, with an optional prefilled message.