DNS Lookup
Find A, AAAA, CNAME, MX, NS, TXT, and SOA DNS records for a host.
DNS Lookup is a free tool that queries a host for A, AAAA, CNAME, MX, NS, TXT, SOA, and CAA DNS records and displays the returned details.
What happens when DNS answers a query?
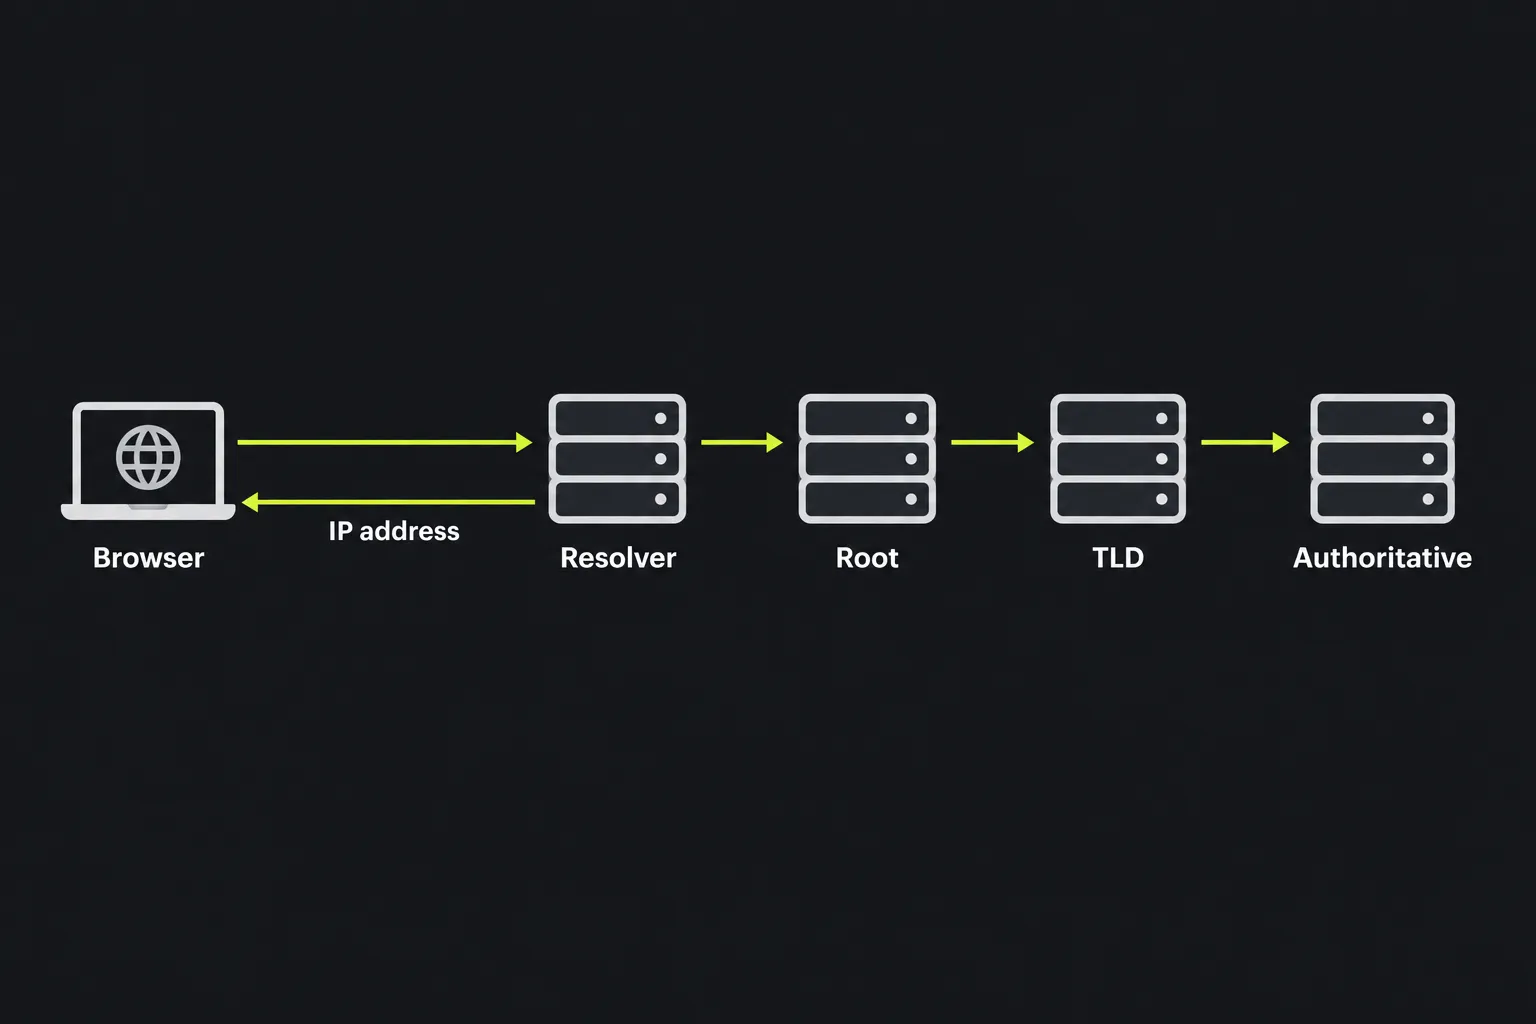
DNS translates a host such as www.example.net into records that describe where its website, email, nameservers, and other services are located. The Domain Name System is distributed, so no single server holds every answer. Iterative resolvers follow referrals through the DNS hierarchy and may cache answers they have already received.
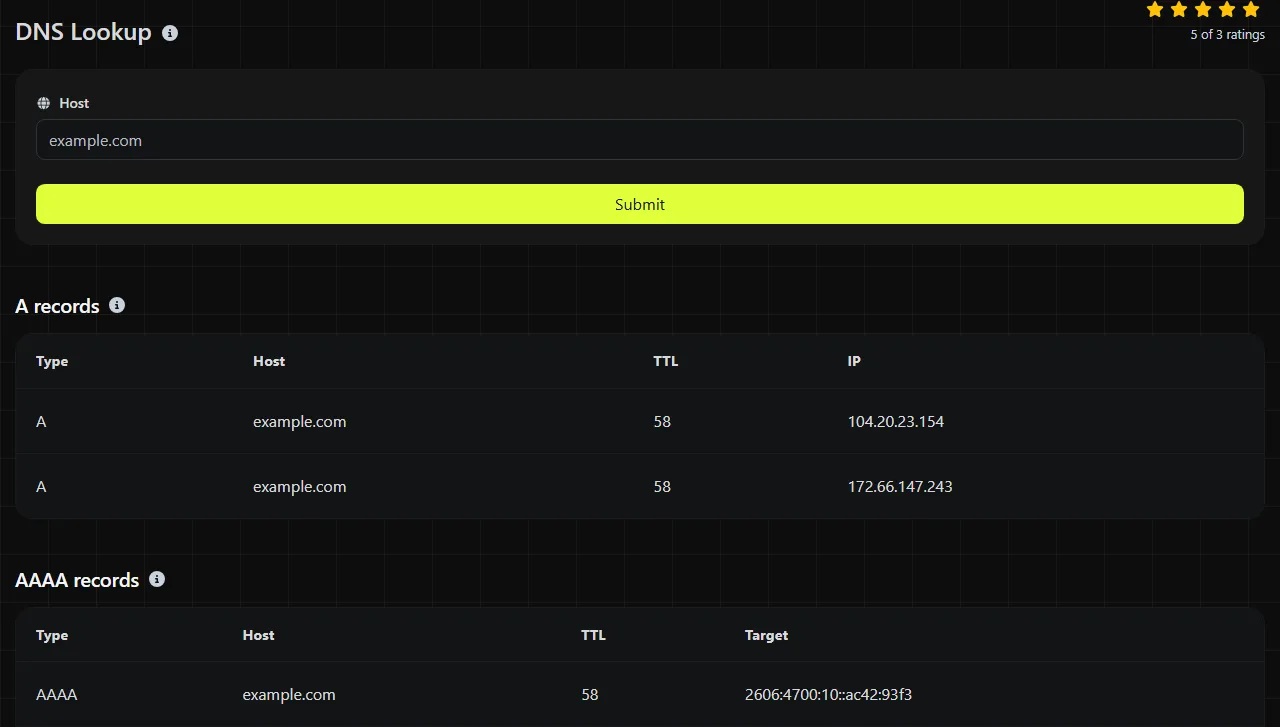
Enter a domain or hostname in the Host field. The lookup runs on the server using the host supplied in the request. Your input travels to the server over HTTPS and is not stored.
Each record type answers a different question. An A record contains an IPv4 address, while an AAAA record contains an IPv6 address. CNAME points one hostname to another. MX identifies mail servers, NS identifies authoritative nameservers, and TXT carries provider verification or policy data. SOA describes the zone's administrative settings. CAA states which certificate authorities may issue certificates for the domain.
Which DNS record should I check?
Check the record connected to the failing service rather than treating every returned row as equally relevant. Use the following guide:
- A or AAAA: Check these when a website or API does not reach the expected server.
- CNAME: Check this when a subdomain should follow another hostname, as with a hosted storefront or support portal.
- MX: Check this when inbound email is delayed, rejected, or delivered to an old provider.
- NS and SOA: Check these after changing DNS hosting or when different resolvers return inconsistent zone data.
- TXT: Check this for SPF, DKIM-related hostnames, DMARC, and ownership verification for services such as Google Workspace or Microsoft 365.
- CAA: Check this when a certificate authority reports that it is not permitted to issue a TLS certificate.
For example, suppose shop.example.net should point to a hosted commerce platform. A CNAME row with a different target would explain why traffic reaches the wrong service. If example.net has an MX record with priority 10 and target mail.example.net, that means mail senders should try that mail host according to its priority relative to any other MX records.
Reading each returned field
The fields shown depend on the record type. Blank or absent fields are normal when they do not apply to a particular record.
| Field | What it tells you |
|---|---|
| Host | The name associated with the returned record. |
| TTL | The record's time to live in seconds, which controls how long a resolver may cache it. |
| Target, IPv6 | The IPv4 address or destination name in Target, depending on the record, or the IPv6 address in IPv6. |
| Priority | The preference value for an MX record. Mail senders normally try lower values before higher values. |
| Entries | The content returned in a TXT record. Long TXT data may consist of multiple DNS character segments. |
| Nameserver | An authoritative nameserver listed by an NS record. |
| MNAME, RNAME | The SOA primary nameserver and the responsible party's mailbox, represented in DNS name form. |
| Serial, Refresh, Retry, Expire, Min. TTL | SOA values used for zone versioning, secondary-server timing, expiration, and negative caching. |
| Flags, Tag, Value | CAA settings. The tag commonly identifies an issuance rule, and the value names the authorized certificate authority or reporting destination. |
A result can contain several rows of the same type. Multiple A or AAAA records may distribute requests across servers. Multiple MX records can provide alternate mail routes. When comparing results, check the complete set rather than only the first row.
How can a DNS result isolate a website, email, or certificate problem?
A DNS result isolates the problem by showing whether public DNS contains the address, mail route, or certificate policy the service expects.
- A website reaches an old server. Look up its A, AAAA, and CNAME records. If the returned address or target is the old destination, correct the record at the authoritative DNS provider. If the authoritative data is correct, cached answers may still be involved.
- Email does not arrive or outgoing email is rejected after a provider migration. Inspect every MX row and its Priority value, then review relevant TXT records. An old MX target can send mail to the former provider, while an incorrect SPF record can affect how receiving systems evaluate outgoing mail.
- Certificate issuance fails with a reported CAA authorization problem. Review the CAA Flags, Tag, and Value fields. For a hypothetical record with tag issue and value ca.example, the record authorizes the named certificate authority. Also inspect issuewild when requesting a wildcard certificate.
This check reports DNS data, but it does not test whether a web server responds, whether an SMTP server accepts mail, or whether a certificate is valid. If an address needs more context after the DNS check, IP Lookup or Reverse IP Lookup may help with the next diagnostic step.
Why can a correct DNS update still appear wrong?
A correct update can appear wrong because recursive resolvers and local systems may keep the previous answer until its TTL expires. Browser DNS caches, operating system caches, home routers, and ISP resolvers can each retain data for different periods.
There is no universal propagation timer. A previous TTL of 86,400 seconds permits caching for up to 24 hours, while a TTL of 300 permits five minutes. Lowering the TTL shortly before a planned migration only helps after caches have learned the lower value. A resolver that already cached the older, longer TTL may continue using it.
Negative answers can also be cached. If someone queried a hostname before it existed, the resolver may temporarily retain the "no such name" response based on the zone's negative-caching settings. Delegation changes can take additional time because parent-zone NS information and child-zone records are cached separately.
Common questions about DNS lookups
Can one hostname have both IPv4 and IPv6 addresses?
Yes. A hostname may have A records for IPv4 and AAAA records for IPv6 at the same time. A client may prefer IPv6 when its network supports it, so an incorrect AAAA record can cause failures even when the A record is correct.
Why does a TXT value look split or quoted?
DNS TXT records can contain multiple character segments that software may display separately or combine. Quotation marks may be presentation syntax rather than part of the intended policy value. When verifying SPF or provider tokens, compare the logical combined value and the exact record name.
How should I enter an internationalized domain name?
Applications convert a Unicode U-label to an ASCII A-label for DNS use; an A-label beginning with xn-- uses Punycode encoding. Software may convert accented or non-Latin names automatically, but support varies. If a Unicode hostname is rejected or gives an unexpected answer, use its xn-- A-label and confirm the conversion with the domain registrar.
Are spaces and URL paths valid in a DNS hostname?
No. A path such as /account/login, a query parameter, and the https:// scheme are parts of a URL rather than a DNS hostname. Enter the host portion, such as portal.example.net; spaces inside a conventional hostname are invalid.
Does the lookup store the host I submit?
No. The lookup is performed on the server, so the host travels to the server over HTTPS, but the input is not stored. Before changing DNS, copy the returned values and compare the record name, target, priority, and TTL with the settings at your authoritative DNS provider.
Similar tools
Popular tools
Create a WhatsApp chat link from a phone number, with an optional prefilled message.