SHA-512 generator
Generate a SHA-512 hash for any string input.
SHA-512 generator is a free tool that converts string input into a 512-bit SHA-512 cryptographic hash.
Why is SHA-512 hexadecimal output 128 characters long?
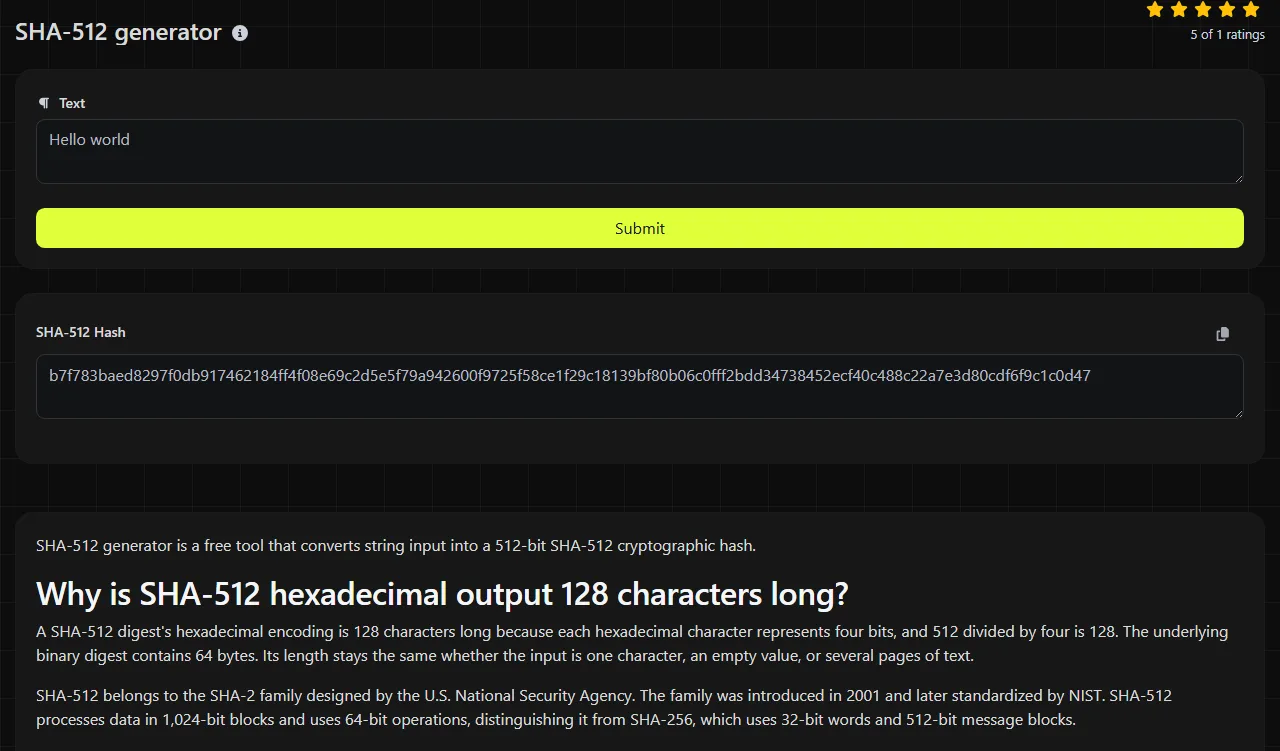
A SHA-512 digest's hexadecimal encoding is 128 characters long because each hexadecimal character represents four bits, and 512 divided by four is 128. The underlying binary digest contains 64 bytes. Its length stays the same whether the input is one character, an empty value, or several pages of text.
SHA-512 belongs to the SHA-2 family designed by the U.S. National Security Agency. The family was introduced in 2001 and later standardized by NIST. SHA-512 processes data in 1,024-bit blocks and uses 64-bit operations, distinguishing it from SHA-256, which uses 32-bit words and 512-bit message blocks.
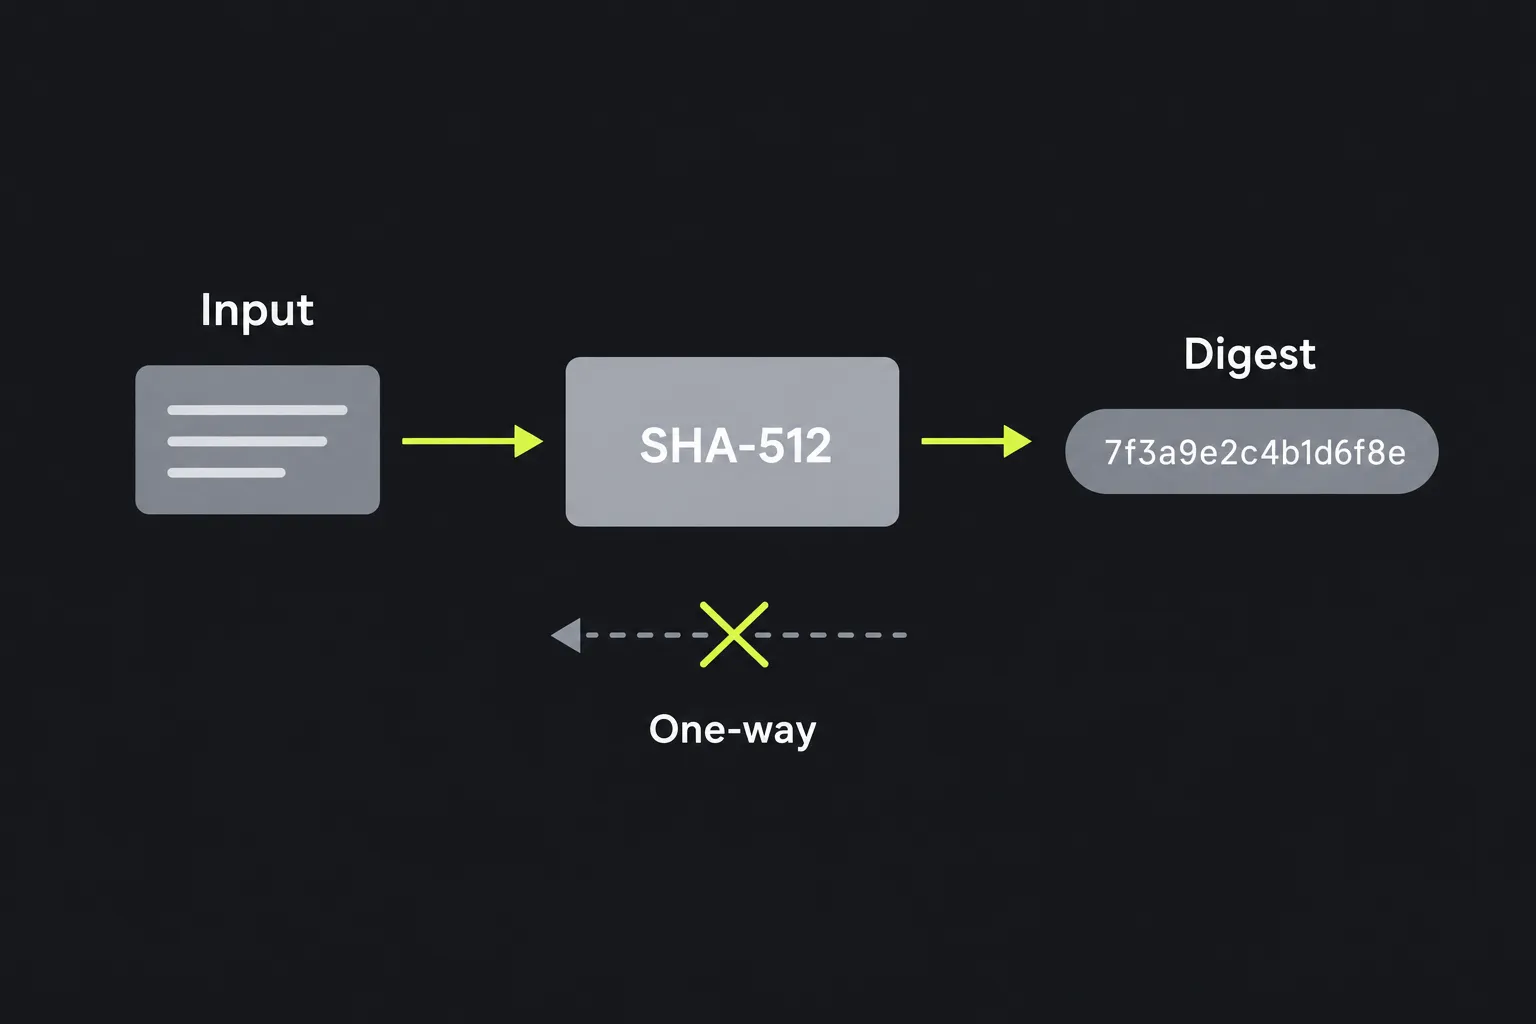
What happens when I submit text?
The tool sends the input to the server over HTTPS, calculates the digest with PHP's hash implementation, and returns the SHA-512 Hash. The input is not stored, but it does leave the device during processing, so do not submit passwords, private keys, access tokens, or other secrets.
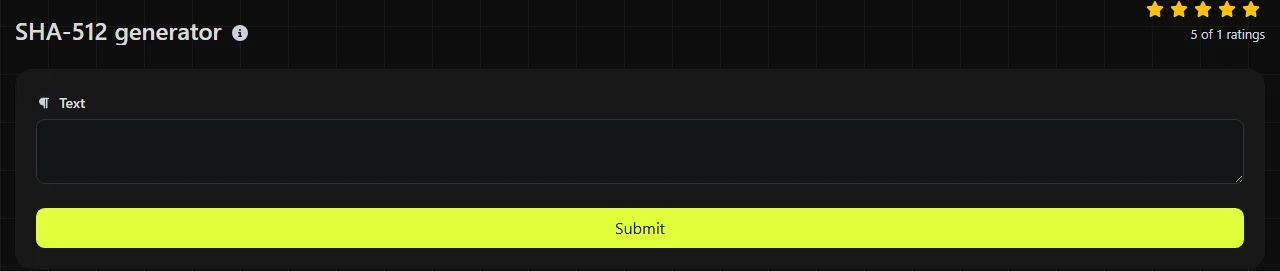
- Enter the exact string to generate its SHA-512 hash.
- Run the generator and copy the returned 128-character hexadecimal value.
- Compare it with the expected SHA-512 hexadecimal output character for character, including any leading zeros.
The generator accepts string input. It is not documented as a file-upload checksum tool, so a command-line utility is a better choice when hashing an installer, archive, disk image, or other binary file.
Byte-level input behavior
SHA-512 operates on bytes, so every space, punctuation mark, line ending, and encoded character affects the result. For example, the inputs Invoice 1047 and Invoice 1047 produce two different 128-character hexadecimal outputs because the second input has a trailing space.
- Numbers entered in a text field are hashed as their character representation. The text 1047 is different from a four-byte binary integer.
- Uppercase and lowercase are distinct. Report.csv and report.csv do not match.
- Accented text can have more than one Unicode representation. Two visually identical versions of résumé may hash differently if their underlying bytes differ.
- Non-Latin text, such as 東京, can be hashed after it is encoded into bytes. Systems must use the same character encoding to reproduce the digest.
- Line endings matter. Text using Windows-style CRLF endings differs from the same visible text using LF endings.
The SHA-512 algorithm defines a digest for empty input and can process very long data.
Is SHA-512 currently secure?
Yes, full SHA-512 is still considered secure for appropriate cryptographic hashing uses and is not known to be broken. No practical collision or preimage attack currently defeats the complete algorithm, and SHA-512 remains part of the current SHA-2 family.
Can SHA-512 be decrypted or reversed? No, there is no decryption operation for a SHA-512 digest. An attacker can still guess possible inputs, hash each guess, and look for a match. That approach is effective against short or predictable values such as common passwords, PINs, and small sets of database identifiers.
SHA-512 has an expected collision resistance of about 256 bits and preimage resistance of about 512 bits under the standard idealized model. Its large digest provides a wider security margin than shorter SHA-2 variants, although a larger digest is not necessary for every checksum or interoperability requirement.
Appropriate and inappropriate uses
SHA-512 fits systems that explicitly require a 512-bit SHA-2 digest. Possible uses include software release checksums, content-addressed storage, duplicate detection, integrity checks, digital signature systems, and legacy formats built around SHA-512.
Do not use a single raw SHA-512 digest to store passwords. SHA-512 is deliberately fast, which lets an attacker test guesses quickly. Password databases should use a dedicated password-hashing function such as Argon2id, scrypt, bcrypt, or PBKDF2 with an appropriate salt and work factor.
A plain SHA-512 digest also does not authenticate a message. Anyone who can change the data can calculate a new digest. Use HMAC-SHA-512 when a shared secret must prove that a message came from an authorized party.
Choose SHA-256 generator when a protocol requires the more common 256-bit SHA-2 output. SHA-384 generator produces a 384-bit digest, while SHA-512/224 generator is a separately defined algorithm with a 224-bit result. SHA-512/224 is not simply a SHA-512 value cut to 224 bits.
Questions people ask about SHA-512
Is SHA-512 faster than SHA-256?
It depends on the processor and implementation. SHA-512 can process large data efficiently on 64-bit CPUs because it uses 64-bit words and larger blocks, but its digest is twice as long.
Can a SHA-512 checksum prove that a download is genuine?
A matching checksum proves that the downloaded bytes match the bytes used to create that checksum. It does not prove who published them if an attacker can replace both the file and the displayed digest. Obtain the SHA-512 checksum from an authenticated source or verify a signed release manifest.
Does copying text from a document change its hash?
It can. Copying may introduce nonbreaking spaces, curly quotation marks, hidden line breaks, or Unicode normalization differences. Check whitespace before comparing SHA-512 outputs across systems.
Can SHA-512 be used to derive an encryption key?
A raw SHA-512 digest is generally not the right key-derivation method. Use a specified key derivation function such as HKDF for high-entropy key material or a password KDF for human-chosen passwords. Follow the encryption protocol's requirements when using a SHA-512-based key derivation function.
Popular tools
Create a WhatsApp chat link from a phone number, with an optional prefilled message.