SHA-512/224 generator
Generate a SHA-512/224 hash for any string input.
SHA-512/224 generator is a free tool that converts string input into a fixed-length SHA-512/224 cryptographic hash.
Why does SHA-512/224 produce a 224-bit result?
SHA-512/224 produces a 224-bit digest because it is a SHA-2 variant designed to use SHA-512's internal structure while returning a shorter result. The digest is 28 bytes long and is commonly displayed as 56 hexadecimal characters.
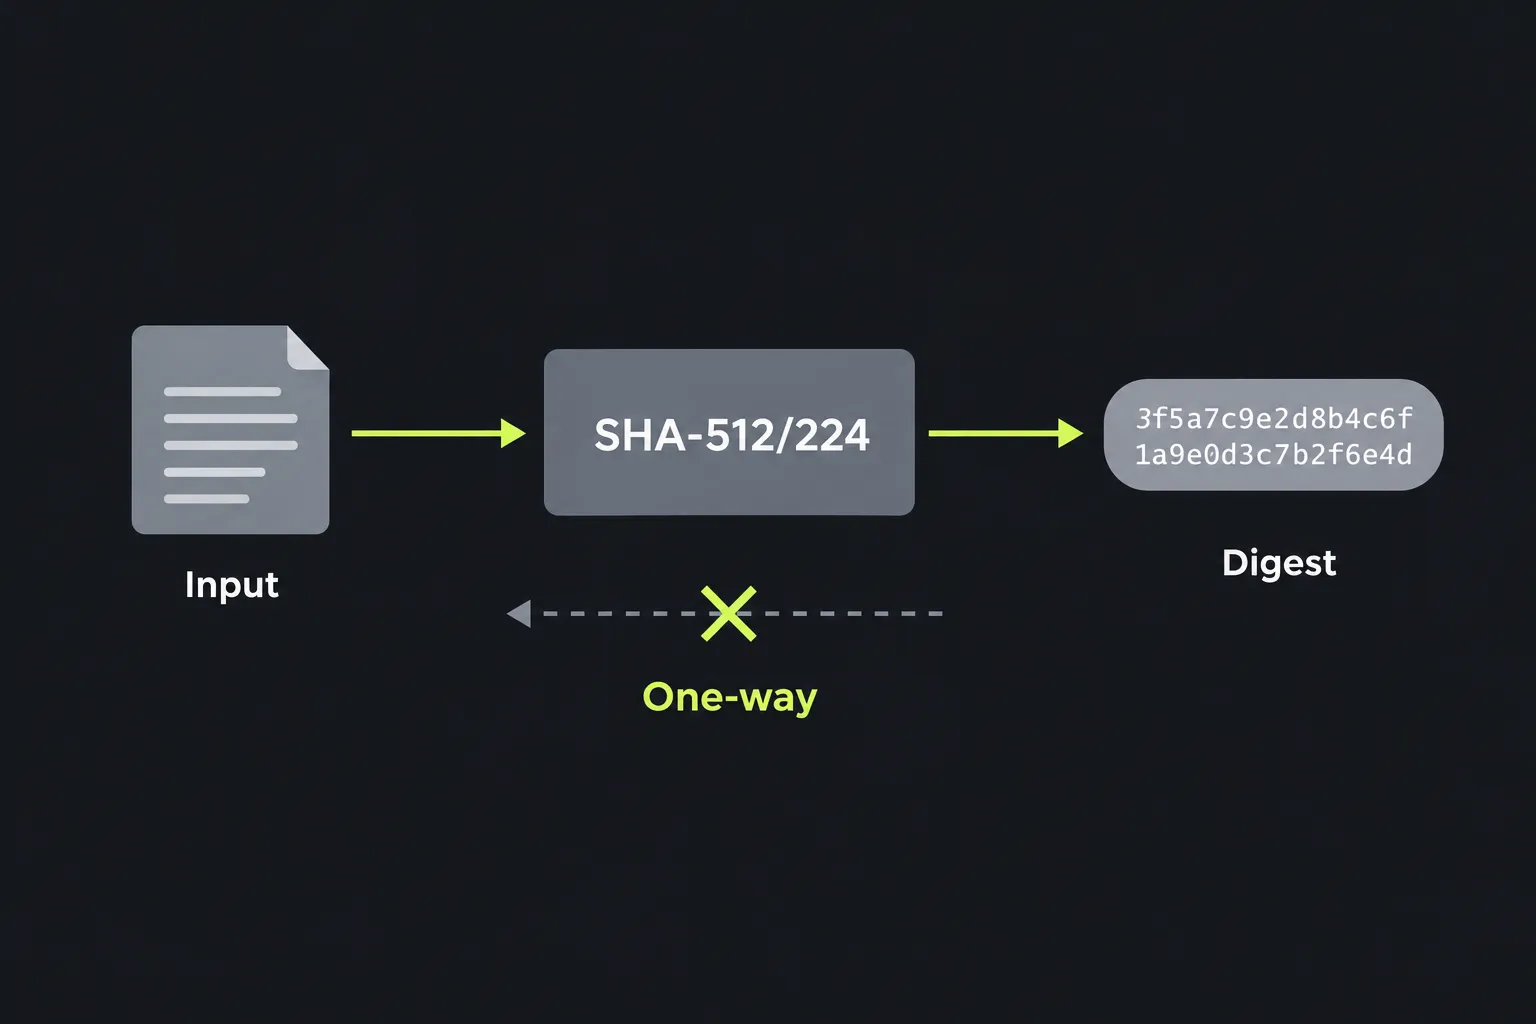
SHA-512/224 creates a fixed-length fingerprint from input data. SHA-512/224 is one-way, so its digest does not contain instructions for reconstructing the original input. Even a small input change produces a different SHA-512/224 result.
The National Institute of Standards and Technology standardized SHA-512/224 in FIPS 180-4 in 2012. It uses SHA-512's 64-bit compression function with initialization values defined specifically for SHA-512/224, then truncates the result to 224 bits. It is therefore not equivalent to taking the first 224 bits of an ordinary SHA-512 digest. It is also different from SHA-224, which is based on SHA-256's internal structure.
SHA-512/224 remains an approved SHA-2 algorithm and has no known practical break against its full design. Its expected collision resistance is about 112 bits because collision attacks generally require work proportional to the square root of the number of possible digests. Although it is still considered secure for appropriate hashing tasks, it is less widely supported than SHA-256, SHA-384, or SHA-512.
How should you use the generated digest?
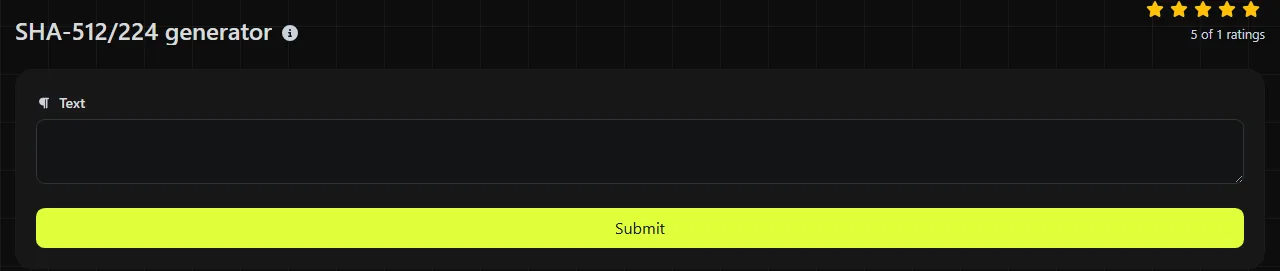
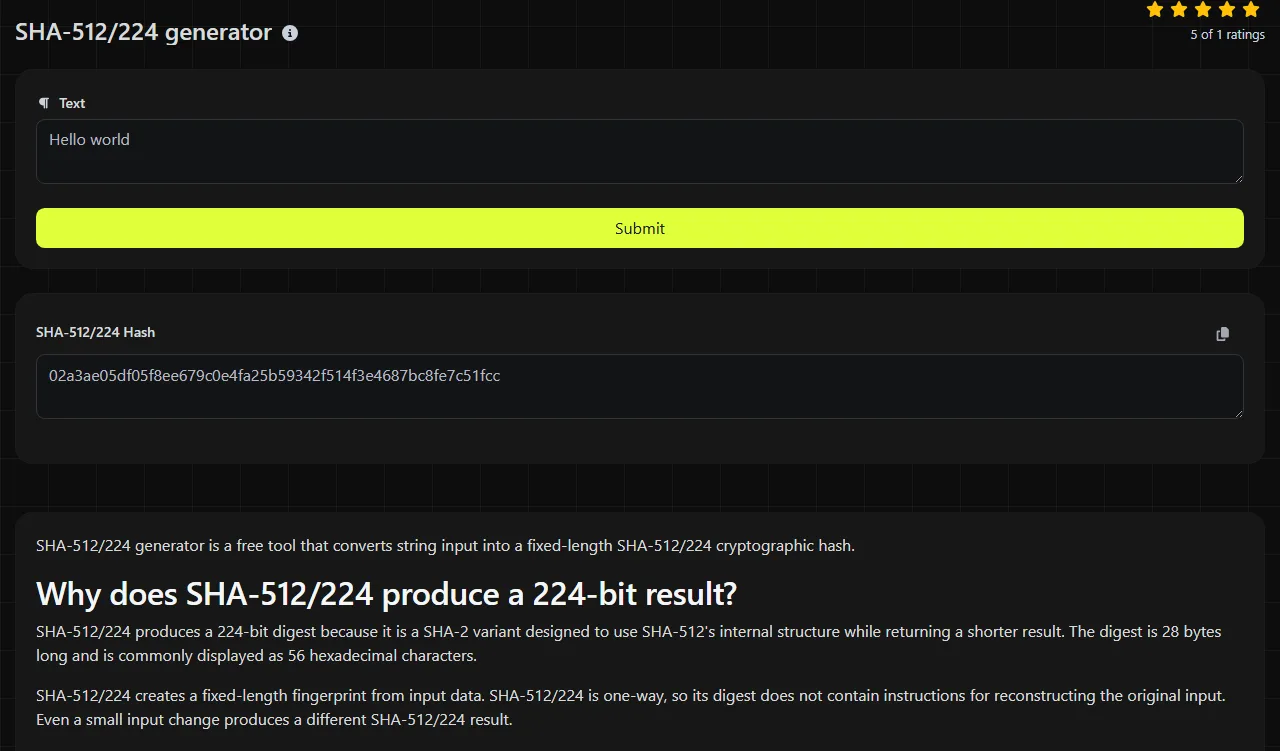
Submit the exact input that another system will hash, then copy the value from SHA-512/224 Hash. A valid displayed result should contain 56 hexadecimal characters, representing 28 bytes.
The calculation happens on the server. Your input travels to the server over HTTPS and is not stored. Do not submit confidential material if your security policy prohibits sending it to an external server, even over an encrypted connection.
For a simple comparison, consider these inputs:
- Input A is Invoice 0042. The output is a 56-character hexadecimal digest.
- Input B is invoice 0042. Its digest differs because the first letter changed from uppercase to lowercase.
- Input C is Invoice 0042 followed by a space. That trailing space becomes part of the input and changes the digest again.
When checking a known value, compare the entire digest rather than a shortened prefix. Confirm that both systems use SHA-512/224 rather than SHA-224 or a manually truncated SHA-512 result.
Where does SHA-512/224 still fit?
SHA-512/224 fits systems that require a 224-bit SHA-2 digest while potentially benefiting from SHA-512's 64-bit internal operations, depending on the platform or implementation. It appears in protocol implementations, compatibility work, checksums, content indexing, and deduplication systems that explicitly name this algorithm.
- Use it to reproduce a checksum supplied by a legacy application or protocol.
- Use it to detect accidental changes when both sides already agree on SHA-512/224.
- Use it as a content fingerprint in a deduplication process that has a plan for handling the very unlikely event of a collision.
- Do not use a plain SHA-512/224 digest to store passwords. It is intentionally fast and has no built-in salt, memory cost, or configurable work factor.
Instead of SHA-512/224 output, password storage requires a dedicated password-hashing function such as Argon2id, scrypt, bcrypt, or PBKDF2 with suitable parameters. For a new general-purpose format that does not require 224-bit output, SHA-512/256 often provides a larger digest while retaining SHA-512-based internals. SHA-384 and the full SHA-512 generator are alternatives when a protocol requests their specific output sizes.
Can a SHA-512/224 hash be decoded back to the input?
No, a SHA-512/224 hash cannot be decrypted or directly reversed because hashing is not encryption. SHA-512/224 uses no key and has no decoding operation that restores the input.
An attacker can still guess candidate inputs, hash each one with SHA-512/224, and compare the results. This works well against predictable values such as common passwords, short PINs, or entries from a word list. A SHA-512/224 digest therefore does not hide low-entropy input, even though the algorithm itself has no reverse function.
Multiple possible inputs also mean that the original input cannot be uniquely reconstructed from the digest alone. SHA-512/224 maps inputs of many different lengths into only 2 to the 224th power possible digest values, so distinct inputs must eventually share a digest. Finding such a collision is considered computationally impractical for SHA-512/224, but the mathematical possibility remains.
Input details that change the hash
SHA-512/224 processes bytes, so every byte in the input matters. Visual appearance alone is not enough to determine whether two byte inputs will produce the same SHA-512/224 digest.
- Spaces, tabs, and line endings are included. Windows-style and Unix-style line endings use different byte sequences.
- Punctuation and capitalization affect the digest. Report.csv and report.csv do not match.
- Accented and non-Latin characters must be encoded into bytes. Different Unicode normalization forms can look identical while producing different hashes.
- Numbers entered as text are hashed as their character representation. The text 42 is two characters, not a binary integer value.
- The SHA-512/224 algorithm defines a digest for empty input. An empty value is different from a single space or an empty line ending with a newline.
- Very long data can be hashed by the algorithm, but an online form may be less suitable than a local command-line or programming-library implementation for large files.
If two applications produce mismatched SHA-512/224 digests, inspect hidden whitespace, line endings, encoding, and normalization before assuming either implementation is wrong.
Questions people ask about SHA-512/224
How strong is SHA-512/224 against collisions?
Its generic collision security is approximately 112 bits. That is lower than SHA-512/256's approximately 128-bit collision security, but no practical collision attack against full SHA-512/224 is known.
Will different programming languages return the same digest?
Yes, conforming implementations return the same digest when they receive identical bytes. Mismatches usually come from whitespace, line-ending, or character-encoding differences; depending on the implementation, automatic newline insertion, Unicode normalization, or hashing a hexadecimal representation instead of the underlying bytes can also cause them.
Can a SHA-512/224 checksum prove who sent data?
No. A plain SHA-512/224 digest can show that data differs from an expected value, but anyone who changes the data can calculate a new SHA-512/224 digest. Sender authentication requires a digital signature or a properly constructed message authentication code with a secret key.
What name do software libraries use for this algorithm?
Names vary by implementation and may include SHA-512/224, SHA512-224, or sha512-224. Check the library's documentation rather than selecting SHA-224 or truncating SHA-512 yourself, since those operations produce different digests.
Is SHA-512/224 suitable for signing certificates?
Only use it when the certificate system, signature format, and every verifier explicitly support the algorithm identifier. Broader interoperability often favors more commonly implemented SHA-2 choices, so verify compatibility before issuing long-lived signed material.
Final checks
Record the algorithm name alongside the digest, preserve leading zeros, and compare all 56 hexadecimal characters. If the value must match another system, test a known sample and confirm the exact input bytes before relying on the result.
Popular tools
Create a WhatsApp chat link from a phone number, with an optional prefilled message.