SHA-3/224 generator
Generate a SHA-3/224 hash for any string input.
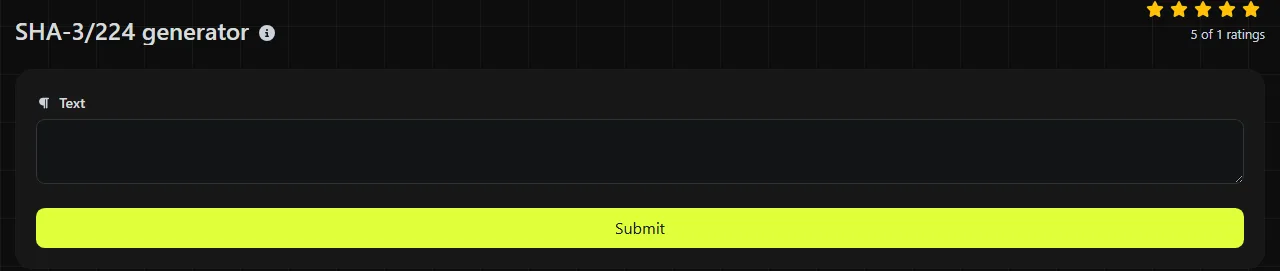
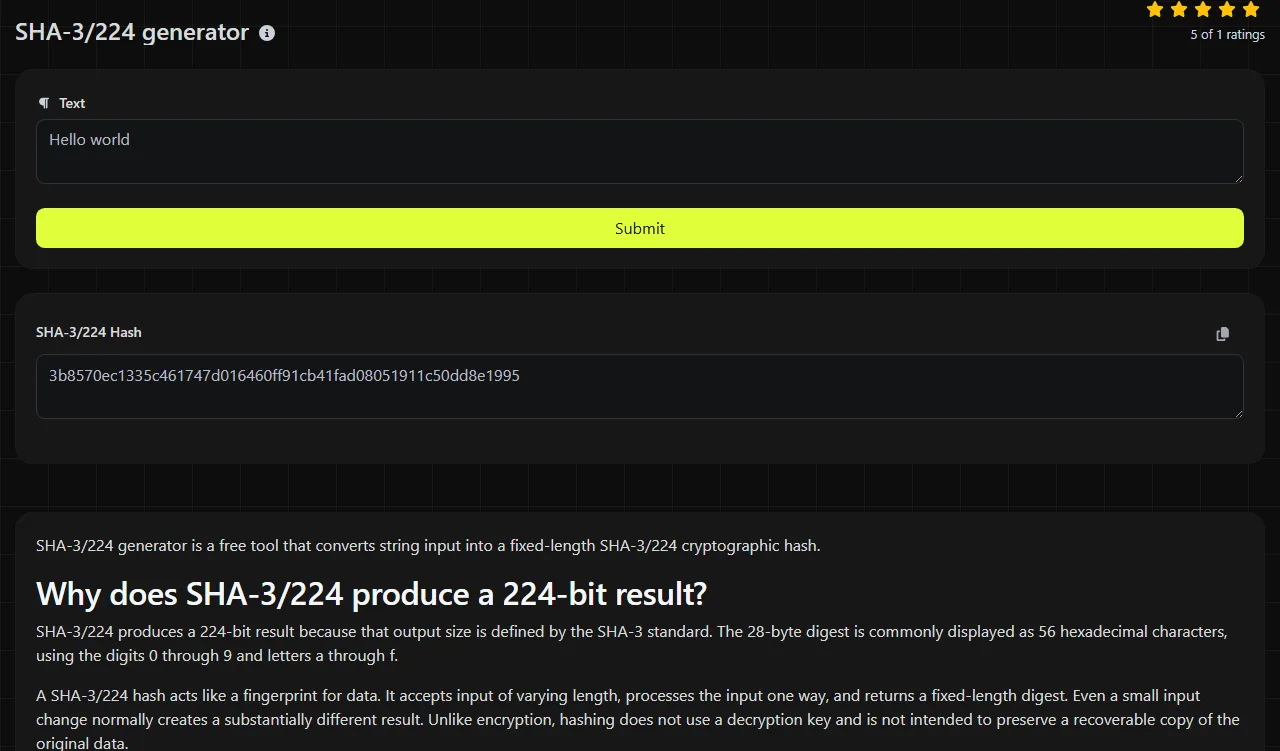
SHA-3/224 generator is a free tool that converts string input into a fixed-length SHA-3/224 cryptographic hash.
Why does SHA-3/224 produce a 224-bit result?
SHA-3/224 produces a 224-bit result because that output size is defined by the SHA-3 standard. The 28-byte digest is commonly displayed as 56 hexadecimal characters, using the digits 0 through 9 and letters a through f.
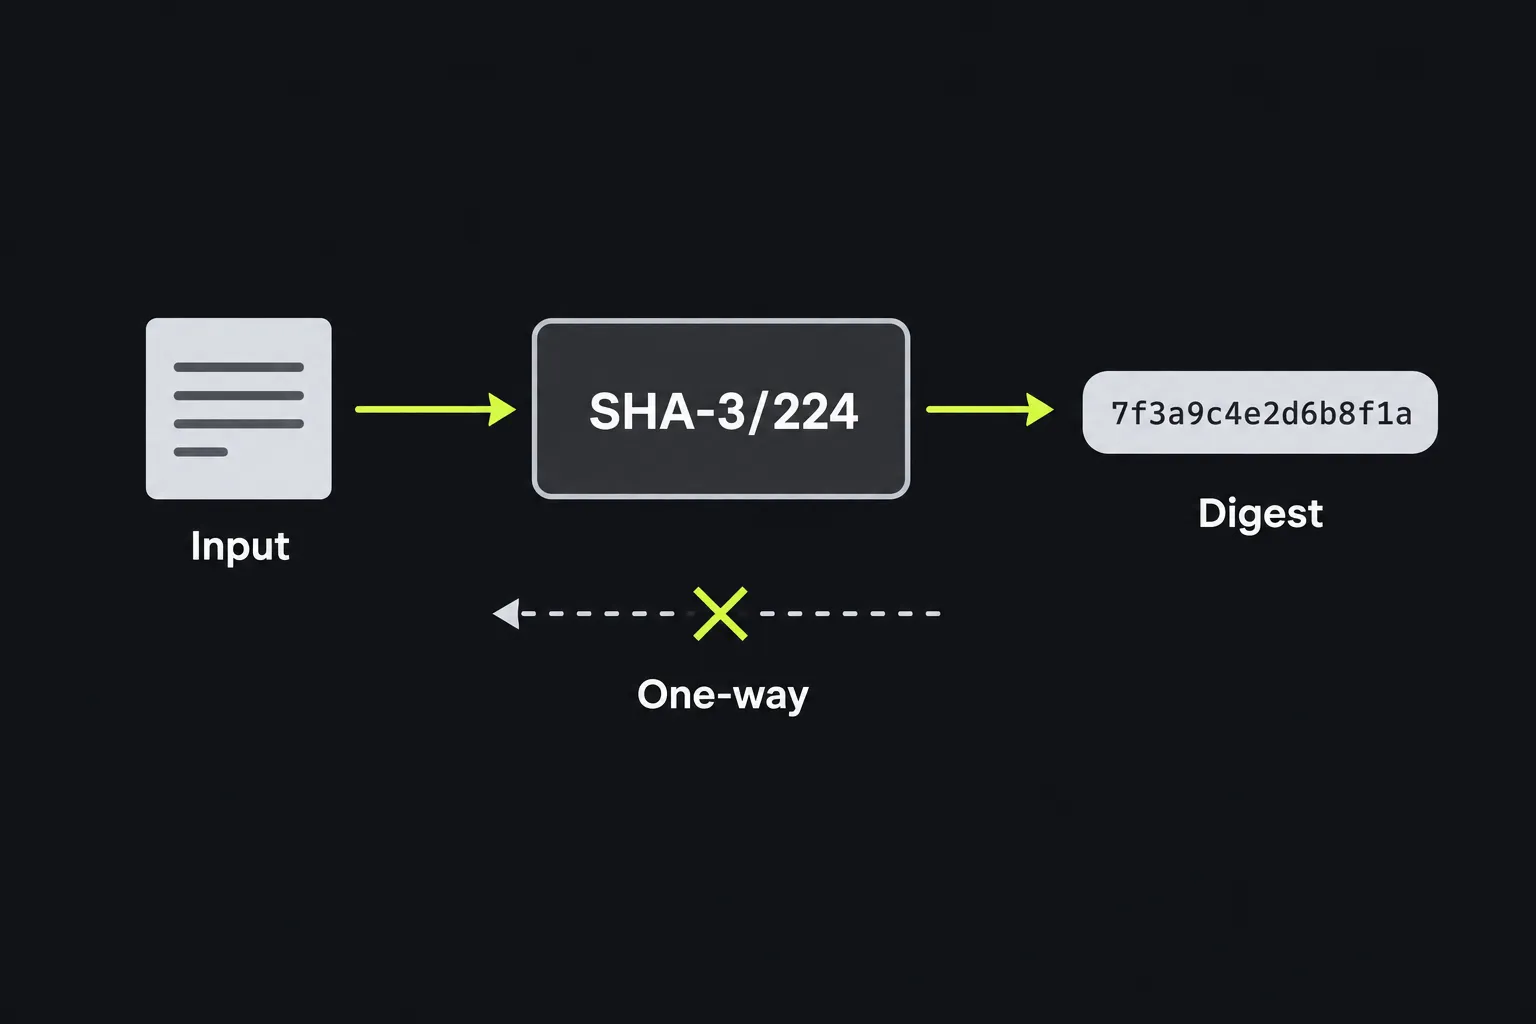
A SHA-3/224 hash acts like a fingerprint for data. It accepts input of varying length, processes the input one way, and returns a fixed-length digest. Even a small input change normally creates a substantially different result. Unlike encryption, hashing does not use a decryption key and is not intended to preserve a recoverable copy of the original data.
SHA-3 is based on Keccak, designed by Guido Bertoni, Joan Daemen, Michaël Peeters, and Gilles Van Assche. NIST selected Keccak for the SHA-3 standard in 2012 and published SHA-3 in FIPS 202 in 2015. SHA-3/224 uses the SHA-3 sponge construction with a 224-bit output.
Can SHA-3/224 be decrypted or reversed? No. There is no decryption operation for a SHA-3/224 digest. Someone can still guess likely inputs, hash each guess, and compare the results, which is why short or predictable secrets remain vulnerable to guessing.
How do I generate and verify a SHA-3/224 checksum?
Enter the exact text to be hashed, generate the result, and copy the value from the SHA-3/224 Hash field. To verify data later, hash the same input again and compare all 56 hexadecimal characters.
- Use the exact characters from the original input, including spaces and line breaks.
- Generate the SHA-3/224 digest.
- Save the SHA-3/224 digest separately from the data if it will be used as a checksum.
- Generate another digest from the data being checked.
- Confirm that the two digests match character for character.
For example, the input Invoice 1042 produces a 56-character hexadecimal digest. Invoice 1042 followed by a space produces a different digest. Unequal digests show that two inputs differ, but matching digests do not prove equality because collisions are possible, and the digest cannot explain what changed.
This tool performs the work on the server. Your input travels to the server over HTTPS and is not stored. Avoid submitting confidential material if sending it to a server conflicts with your organization's data-handling rules.
Where does SHA-3/224 make sense today?
SHA-3/224 makes sense when a specification requires that exact algorithm or when a 224-bit SHA-3 digest is already part of an existing data format. It remains a current cryptographic hash, and there is no practical break known against the full SHA-3/224 algorithm.
Its 224-bit output provides about 112 bits of generic collision resistance. That is the expected work factor for finding any two different inputs with the same digest. Preimage resistance, which concerns finding an input for a given digest, has a higher generic classical work factor.
- SHA-3/224 checksums can identify accidental changes when the expected digest comes from a trusted source.
- Deduplication systems can use the digest as a compact candidate identifier, then compare the underlying data when exact equality matters.
- Legacy compatibility may require SHA-3/224 when a stored record, protocol, or partner system already uses it.
- Reproducible records can include a digest to identify the exact bytes used for a report, export, or build input.
For a new design without a fixed 224-bit requirement, SHA-3/256 is often the more interoperable choice and has a larger security margin. SHA-512/224 and SHA-512/256 have similar-looking names but belong to the SHA-2 family, so they do not produce interchangeable results.
Input details that change the digest
SHA-3 hashes bytes, so every byte in the input matters. SHA-3/224 processes numbers and punctuation as ordinary data. They do not receive mathematical or grammatical interpretation.
- Report7 and report7 differ because letter case changes the input.
- Order #408 and Order#408 differ because one contains a space.
- A final line break changes the digest even when it is hard to see in a text editor.
- Accented and non-Latin characters are converted to bytes by a character encoding, commonly UTF-8. Visually identical Unicode text can have different byte representations.
- The SHA-3 algorithm defines a digest for an empty byte sequence, although an interface may treat a blank field as missing input.
- SHA-3 can process very long input, but an online form can still be constrained by browser, request, or server limits.
If two systems disagree, inspect hidden whitespace and line-ending differences and confirm that both systems selected SHA-3/224 rather than SHA-224 or SHA-512/224 before assuming either implementation is wrong. If the systems may encode the text differently, also compare the input encoding.
Should SHA-3/224 be used to store passwords?
No, SHA-3/224 should not be used by itself to store passwords. It is designed to hash data quickly, which also lets an attacker test password guesses quickly after obtaining a password database.
Instead of SHA-3/224, password storage requires a purpose-built password hashing function with a unique salt and a configurable work factor. Common choices include Argon2id, scrypt, bcrypt, and PBKDF2 when required by a platform or compliance profile. A plain SHA-3/224 digest is also unsuitable for authentication because anyone who can change the data can calculate a new unkeyed digest. Use a message authentication code or a digital signature when the result must prove who authorized the data.
Questions people often ask about SHA-3/224
Can I shorten a SHA-3/224 hash before storing it?
You can technically truncate a digest, but doing so reduces its resistance to collisions and breaks compatibility with systems expecting the full 56-character value. Store the complete digest unless a documented protocol specifies a shorter representation.
Is SHA-3/224 the same as a SHAKE output set to 224 bits?
No. SHAKE functions use a different domain separation value and support variable-length output. A 224-bit SHAKE result will not match SHA-3/224 for the same input.
Does a SHA-3/224 checksum prove when a document was created?
No. A digest identifies data but contains no trusted creation time. Proving that data existed at a particular time requires a separate trusted timestamp, a signed record with independently trustworthy time evidence, or comparable evidence.
Can I calculate SHA-3/224 from the command line?
Yes, if the installed cryptographic software includes SHA-3/224 support. SHA-3/224 algorithm names and syntax vary by operating system and package version, so check the program's supported digest list before relying on a command in an automated workflow.
Should I add a salt to a checksum?
Usually no. A salt can make identical inputs produce different results when different salts are used and must be retained to reproduce the digest, which works against ordinary checksum comparison. Salts belong primarily in password hashing and certain privacy-sensitive indexing schemes, not routine file integrity checks.
Popular tools
Create a WhatsApp chat link from a phone number, with an optional prefilled message.