SHA-256 generator
Generate a SHA-256 hash for any string input.
SHA-256 generator is a free tool that converts string input into a 256-bit SHA-256 hash shown as hexadecimal text.
Why was SHA-256 created, and is it still secure?
SHA-256 was created as part of the SHA-2 family to provide a stronger successor to older hash functions, and it is still considered secure for general cryptographic hashing. The U.S. National Security Agency designed SHA-2, and the National Institute of Standards and Technology published it in 2001.
SHA-256 produces a 256-bit, or 32-byte, digest. It is commonly written as 64 hexadecimal characters because each hexadecimal character represents four bits. Its fixed output size does not change when the input becomes longer.
No practical collision or preimage attack against full SHA-256 is publicly known. A generic collision search would require roughly 2 to the 128th power operations, while a generic preimage search would require roughly 2 to the 256th power. That security status differs from SHA-1, which has practical collision attacks and should not be selected for new security-sensitive systems.
What happens when you submit text?
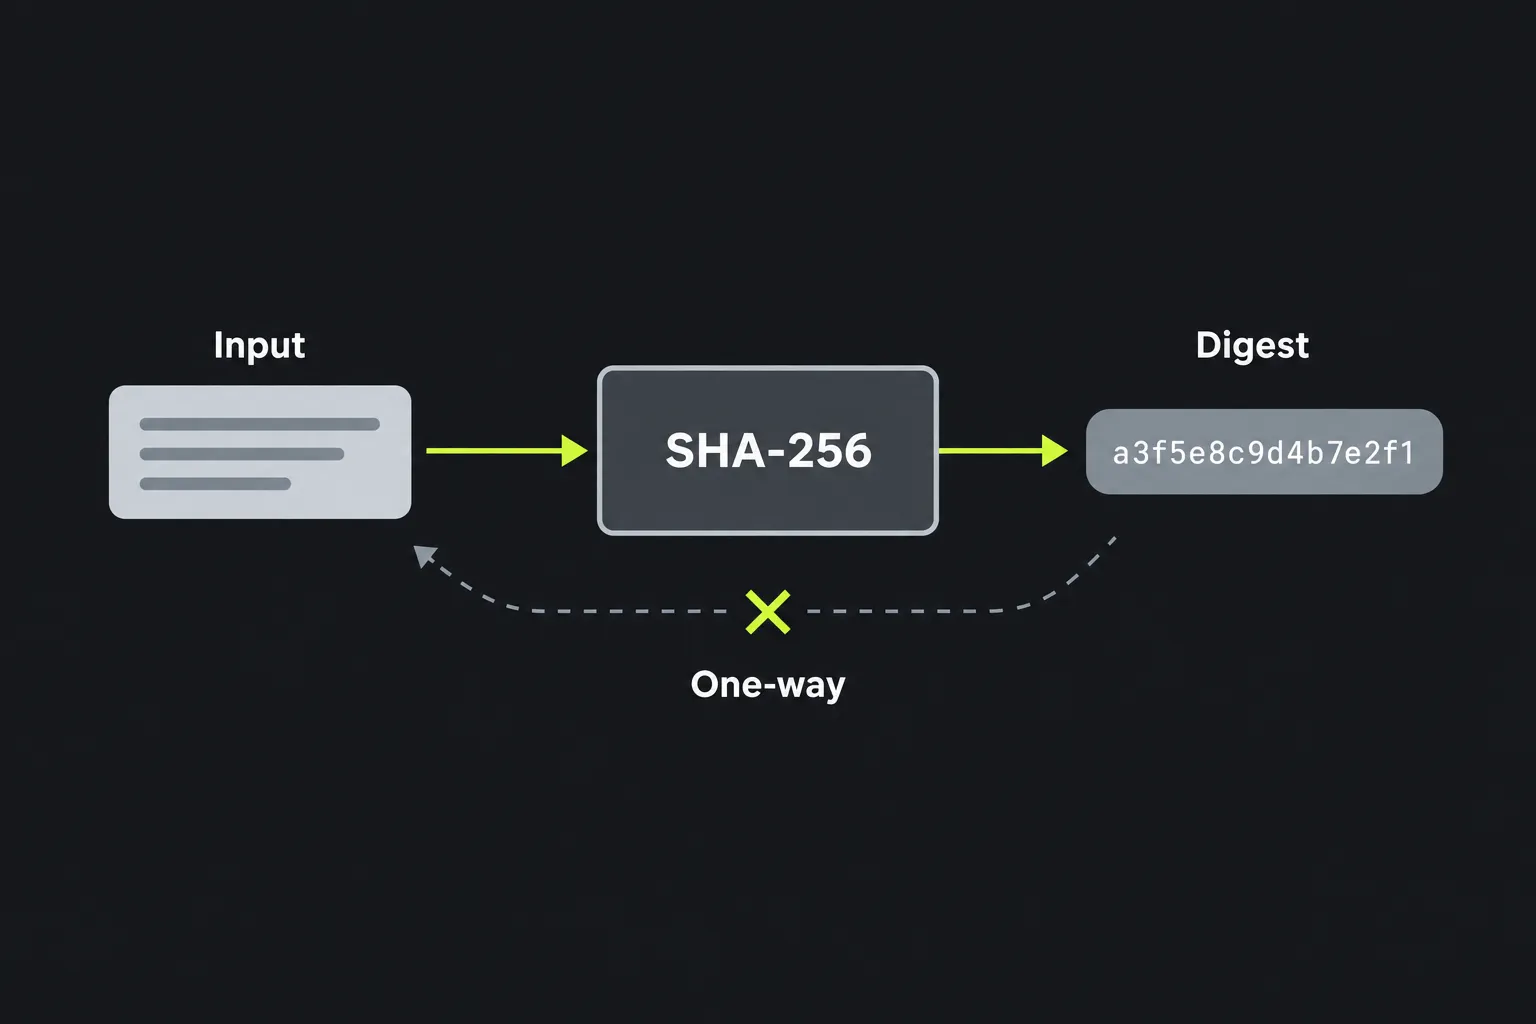
The tool sends the input to the server over HTTPS, calculates the digest with the server-side PHP hash function, and returns the result in the SHA-256 Hash field. The input is not stored, but it does travel to the server, so avoid submitting secrets that should not leave your device.
A SHA-256 hash from this tool is a fixed-length fingerprint of data. It is designed to work in one direction, from input bytes to a digest, without providing a decryption key or a built-in way to recover those bytes. The same bytes produce the same digest, while even a small input change normally produces a very different result.
For example, the text Invoice 10482 produces a 64-character hexadecimal result. Adding one trailing space still produces a 64-character result, but the digest changes because the input bytes changed. Empty input is also valid and has its own SHA-256 digest.
Why do two SHA-256 results fail to match?
Two SHA-256 results from this tool usually fail to match because the underlying bytes differ, even when the displayed text looks similar. Check the original data rather than editing the digest.
- Spaces and line endings: A leading space, trailing newline, Windows CRLF line ending, or Unix LF line ending changes the hash.
- Letter case: Report.csv and report.csv are different inputs.
- Numbers: Text such as 0012 is hashed as four characters and does not match 12.
- Character encoding: Accented letters, emoji, and non-Latin writing are converted to bytes using an encoding such as UTF-8. Different encodings can produce different digests.
- Unicode normalization: Some characters can be represented by more than one valid sequence of Unicode code points. They may look identical while hashing differently.
- Copied formatting: Quotation marks, tabs, byte-order marks, and hidden characters copied from an editor may become part of the input.
Very long input still yields 64 hexadecimal characters, although processing time depends on the amount of data. When comparing a value from another program, confirm that both sides hash the same bytes and display the digest in the same format.
Practical uses and firm boundaries
SHA-256 is commonly used for file checksums, content-based identifiers, deduplication, integrity checks, and compatibility with systems that specify SHA-256. Software publishers may provide a SHA-256 checksum so recipients can detect an incomplete or altered download. Storage systems can compare digests before retaining duplicate content, although they may still compare the actual files before deleting data.
SHA-256 must not be used by itself to store passwords. It is intentionally fast, which lets an attacker test large numbers of password guesses. Password storage requires a dedicated password-hashing function with a salt and a configurable work factor, such as Argon2id, scrypt, bcrypt, or PBKDF2 when required by an existing standard.
A plain SHA-256 digest also does not authenticate who created a message. Use HMAC-SHA-256 when two parties share a secret key, or use a digital signature when recipients need public-key verification. The digest generated here contains no secret key and provides no encryption.
What does a matching hash actually prove?
A matching SHA-256 hash is strong evidence that two inputs contain the same bytes, provided the expected hash came from a trustworthy source. It does not prove who supplied the input or when it was created.
Can SHA-256 be decrypted or reversed? No. SHA-256 is not encryption, and it has no decryption operation. However, an attacker can guess likely inputs, hash each guess, and compare the results. Short values, common passwords, phone numbers, and predictable identifiers can therefore be discovered without reversing the algorithm itself.
A checksum posted beside a download cannot detect a malicious replacement if an attacker can replace both the file and the posted checksum. For higher-risk distribution, obtain the expected digest through a separate trusted channel or verify a signed release.
Questions people ask about SHA-256
Should I choose SHA-224, SHA-256, or SHA-384?
Choose the algorithm required by the system or protocol you are working with. SHA-256 is a common default when no specific SHA-2 variant is mandated. A SHA-224 generator provides a shorter 224-bit digest, while a SHA-384 generator is appropriate when a specification requires its wider output.
Can I store a SHA-256 result in a database?
Yes. The displayed hexadecimal form fits in 64 ASCII characters and can be stored in a fixed-length character column. Systems that convert the digest to raw binary can store the same value in 32 bytes, but the hexadecimal and binary representations must not be compared directly.
Is it safe to publish a SHA-256 checksum?
Publishing a checksum is generally appropriate for software packages and other large, nonsecret files. Be more careful with hashes of predictable private values because someone can test guesses against the published digest. Hashing does not anonymize a small or easily guessed data set.
Does SHA-256 protect the original data while it is being sent?
No. A hash does not encrypt data or provide transport security. This page sends input to the server over HTTPS, but for highly sensitive material, use a local hashing command or approved internal system so the original input stays within the required security boundary.
Popular tools
Create a WhatsApp chat link from a phone number, with an optional prefilled message.