SHA-1 generator
Generate a SHA-1 hash for any string input.
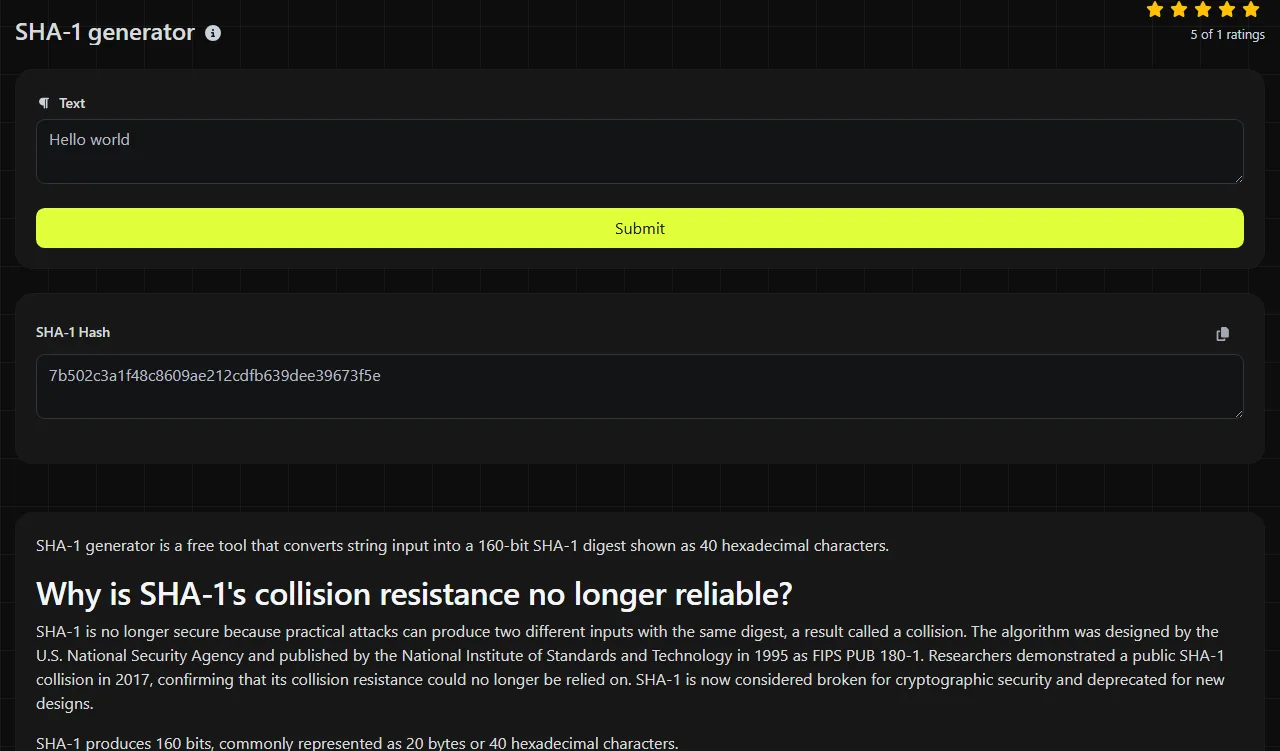
SHA-1 generator is a free tool that converts string input into a 160-bit SHA-1 digest shown as 40 hexadecimal characters.
Why is SHA-1's collision resistance no longer reliable?
SHA-1 is no longer secure because practical attacks can produce two different inputs with the same digest, a result called a collision. The algorithm was designed by the U.S. National Security Agency and published by the National Institute of Standards and Technology in 1995 as FIPS PUB 180-1. Researchers demonstrated a public SHA-1 collision in 2017, confirming that its collision resistance could no longer be relied on. SHA-1 is now considered broken for cryptographic security and deprecated for new designs.
SHA-1 produces 160 bits, commonly represented as 20 bytes or 40 hexadecimal characters.
Do not use SHA-1 for digital signatures, certificates, authentication tokens, or password storage. Instead of using this SHA-1 generator for passwords, use a deliberately slow password-hashing function such as Argon2id, scrypt, bcrypt, or PBKDF2, with a unique salt for each password.
How can I get a repeatable SHA-1 digest?
Enter the exact text you want to hash and generate the result, then copy the value from SHA-1 Hash. The same sequence of bytes produces the same digest every time. Even a one-character change normally produces a different result.
For example, the input "invoice-2026-09-16" produces a 40-character hexadecimal digest. "Invoice-2026-09-16" is a different input because the uppercase I changes the underlying bytes. The output still contains 40 hexadecimal characters.
The calculation happens on the server. Your input travels to the server over HTTPS and is not stored. Because this SHA-1 generator processes input on the server, avoid submitting passwords, private keys, access tokens, or other secrets.
Input details that change the result
SHA-1 processes bytes exactly as supplied. It does not understand words, numbers, or visual formatting, so small input differences matter.
- Spaces and line breaks: "PO 1042" differs from "PO1042." A trailing space or final newline also changes the digest.
- Numbers: Numbers entered into this SHA-1 generator are received as string input and hashed as characters. "00123" and "123" therefore produce different values.
- Punctuation and case: Commas, quotation marks, hyphens, and letter case are part of the SHA-1 byte input processed by this tool.
- Accented and non-Latin text: SHA-1 sees encoded bytes. To match this generator's SHA-1 output, another implementation must use the same character encoding and Unicode normalization.
- Empty input: The SHA-1 algorithm defines a valid digest for an empty byte sequence. An empty value should not be confused with omitted or unavailable data.
- Long input: The digest remains 160 bits even when the input is long. This page does not state a maximum accepted input size, so use file-oriented software for large files or data sets.
Decryption, reversal, and guessed inputs
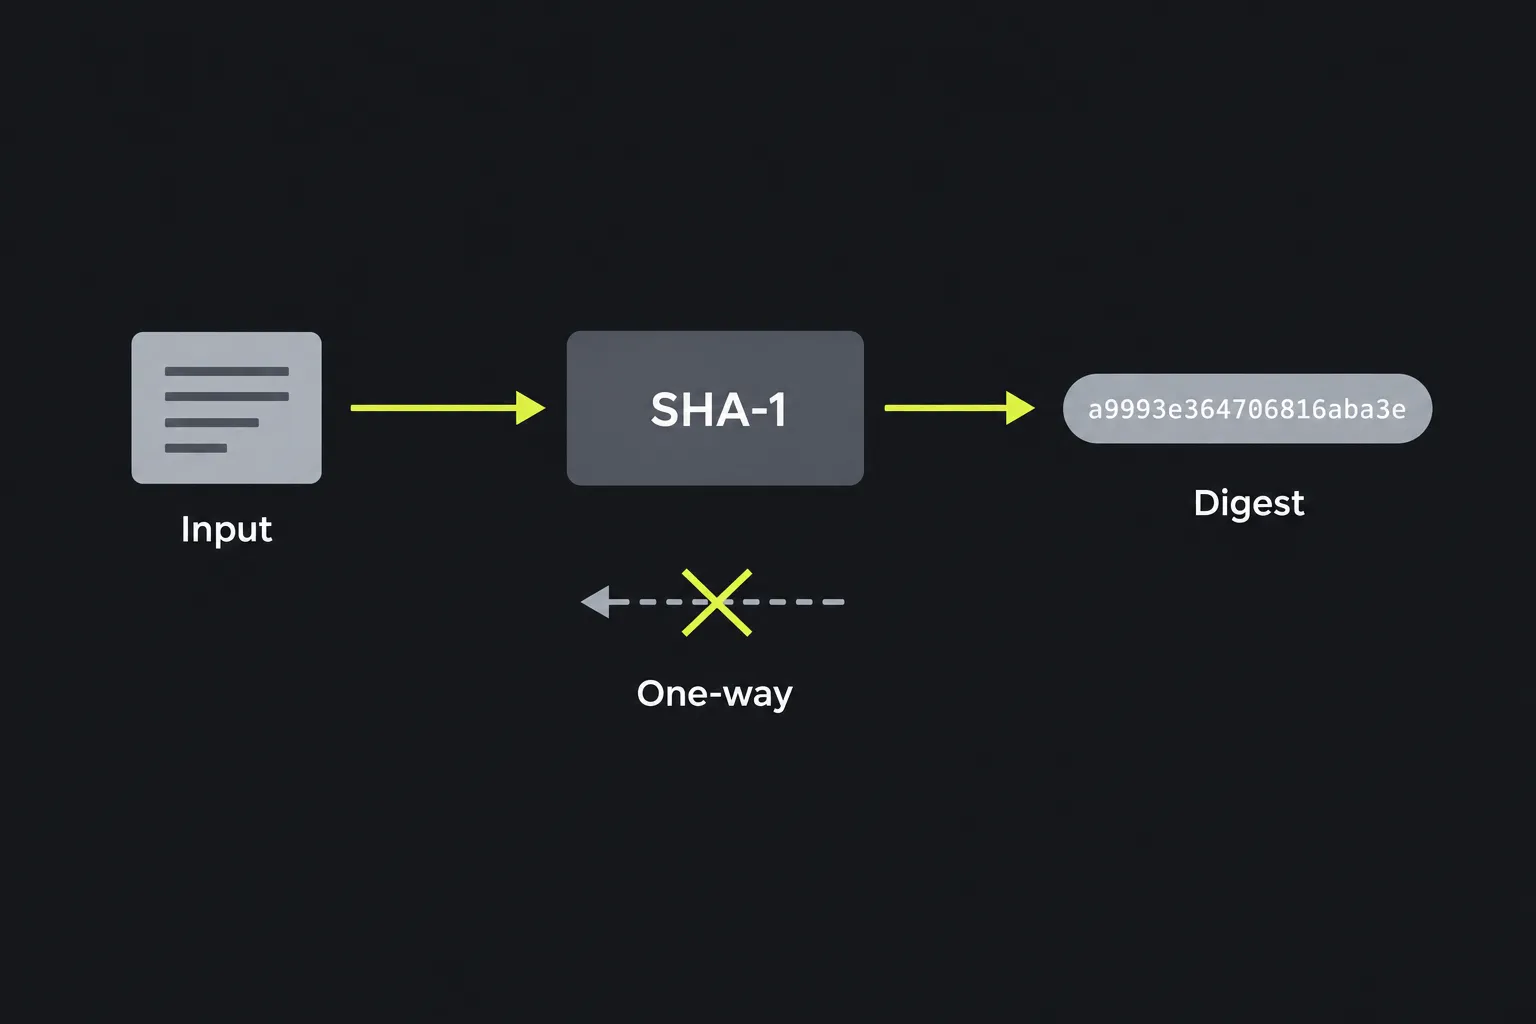
SHA-1 cannot be decrypted or directly reversed because hashing is not encryption and SHA-1 has no decryption key. A 160-bit SHA-1 digest does not preserve enough information to reconstruct an arbitrary original input.
That does not make a SHA-1 value private. An attacker can hash likely inputs and compare the results. Short passwords, common email addresses, phone numbers, and predictable identifiers can often be discovered through dictionary or brute-force guessing. Collision attacks are a separate issue. They find different inputs with the same digest rather than recovering a specific original input.
Does a checksum need collision resistance?
Collision resistance or second-preimage resistance may matter when an attacker could intentionally modify the data, but an unkeyed checksum cannot authenticate data if the attacker can alter both the data and checksum. For accidental-corruption checks or an internal, non-adversarial comparison, that protection may not be needed. Use a MAC or digital signature when authentication is required. SHA-1 still appears in older systems because it is deterministic, widely implemented, and compatible with historical records.
Reasonable present-day uses are limited to situations such as:
- Checking accidental corruption against a SHA-1 value supplied by a legacy source
- Finding probable duplicates in a controlled data set where malicious input is not a concern
- Reproducing identifiers required by an older protocol, archive, or database
- Verifying historical records that cannot change their stored hash format
For a new security-sensitive format, choose a SHA-2 or SHA-3 algorithm instead. The SHA-224 generator can produce a 224-bit SHA-2 digest when a specification specifically requires that size. SHA-256 is more commonly selected for new general-purpose checksum systems.
Common questions about SHA-1
Can a SHA-1 hash safely anonymize an email address?
No. Email addresses have a predictable structure and can be tested against a hash quickly, especially when an attacker has a candidate list. Use a purpose-designed pseudonymization process with controlled secret-key management when identities must be protected.
How much database space does a SHA-1 value require?
The raw digest requires 20 bytes. Its usual hexadecimal representation requires 40 ASCII characters, so databases commonly use a 40-character text column or a 20-byte binary column. Applications comparing values must agree on which representation is stored.
Can file metadata affect a SHA-1 checksum?
When interpreting a SHA-1 file checksum, only bytes included in the hashed data affect the digest. A file's name, location, modification date, and permissions are normally excluded when software hashes file contents, but archive formats may embed metadata inside the archive bytes.
How can I calculate a SHA-1 file checksum locally?
Common command-line options include sha1sum on many Linux systems, shasum -a 1 on macOS, and Get-FileHash -Algorithm SHA1 in PowerShell. Unlike this server-based string-input generator, local commands calculate the checksum on the user's system, so files do not need to be submitted to a website.
Does hashing with SHA-1 twice fix its security problems?
No. Applying SHA-1 repeatedly does not restore the collision resistance expected from a current cryptographic hash. It also does not turn SHA-1 into a suitable password-hashing function, because general-purpose hashes are designed to run quickly.
Checks before relying on the digest
Before comparing another value with this tool's 40-character SHA-1 output, confirm the required algorithm, input encoding, whitespace, and output representation. Use SHA-1 only when compatibility requires it or when deliberate collisions are outside the threat model. For new authentication, signing, password, or integrity systems, select an algorithm intended for that specific job.
Popular tools
Create a WhatsApp chat link from a phone number, with an optional prefilled message.