HTTP headers lookup
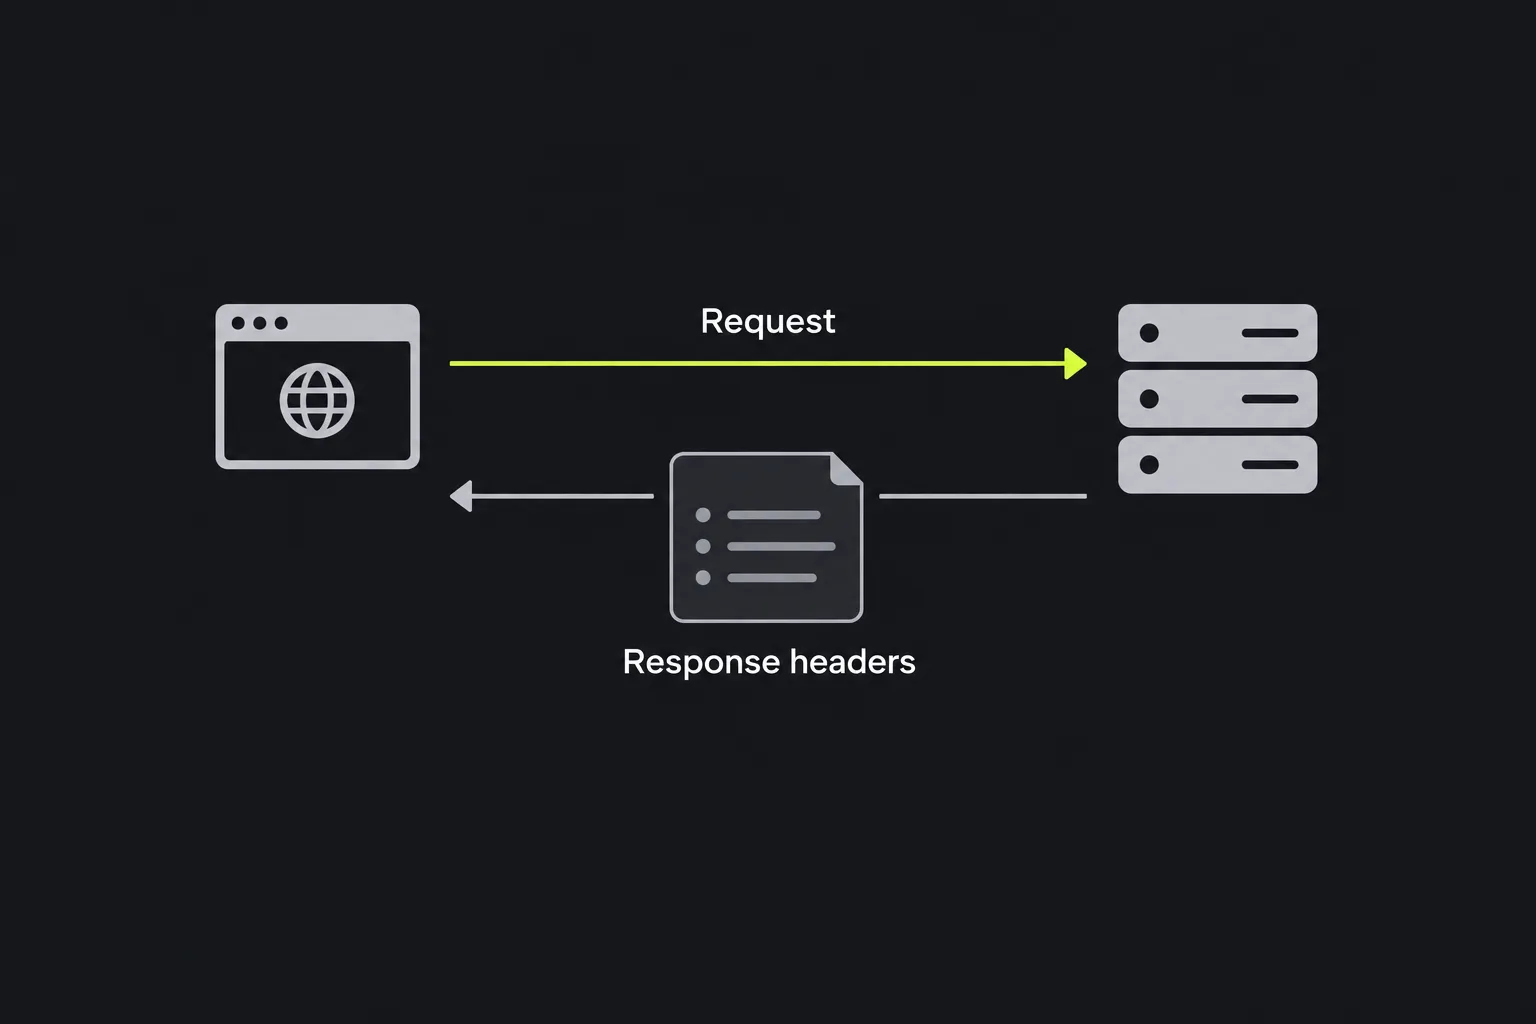
Get all HTTP headers returned by a URL for a typical GET request.
HTTP headers lookup is a free tool that sends a typical GET request to a URL and retrieves all HTTP response headers returned by the server.
What does an HTTP GET reveal about a URL?
An HTTP GET asks a web server for the resource identified by a URL, and the response headers can describe how clients should handle that response, provide metadata, or report diagnostics. Headers are name-and-value fields in the response that can describe response content, when present, such as an HTML page, image, API result, or downloadable file.
They can identify the content format, caching rules, redirect destination, compression method, cookie instructions, and browser security policies. Some headers are defined by HTTP standards, while others are specific to a CDN, hosting provider, proxy, or application.
The exact URL can determine which HTTP response headers the server returns. These addresses can return different headers even when they appear to lead to the same website:
- http://example.com
- https://example.com
- https://www.example.com
- https://example.com/account?preview=1
A URL fragment such as #pricing is not sent in an HTTP request, so it does not affect the server's headers. Query parameters are sent and may change the response, caching behavior, or selected content.
Which header lines should I inspect first?
Start with the headers connected to the problem you are investigating, since many responses contain fields that are unrelated to the immediate issue. Header names are case-insensitive, and a field may be absent when the server has no reason to send it.
| Header | What it tells you |
|---|---|
| Content-Type | The media type and sometimes the character encoding, such as text/html; charset=utf-8 or application/json. |
| Content-Length | The response body size in bytes when the server supplies a known length. Its absence does not mean the body is empty. |
| Content-Encoding | The representation codings applied to the content, often for compression, such as gzip or br. |
| Location | The destination supplied with a redirect or the URI of a newly created resource in a 201 response. |
| Cache-Control | Instructions for browsers and shared caches, including how long a response may be reused. |
| Age | The sender's estimate of the time, in seconds, since the response was generated or successfully validated by the origin server. |
| ETag or Last-Modified | Validators that clients can use to check whether cached content has changed. |
| Set-Cookie | Instructions asking the client to create or update a cookie. Several Set-Cookie lines may appear in one response. |
| Strict-Transport-Security | A policy telling supporting browsers to use HTTPS for the host for a stated period. |
| Content-Security-Policy | Rules limiting where a browser may load scripts, styles, images, frames, and other resources. |
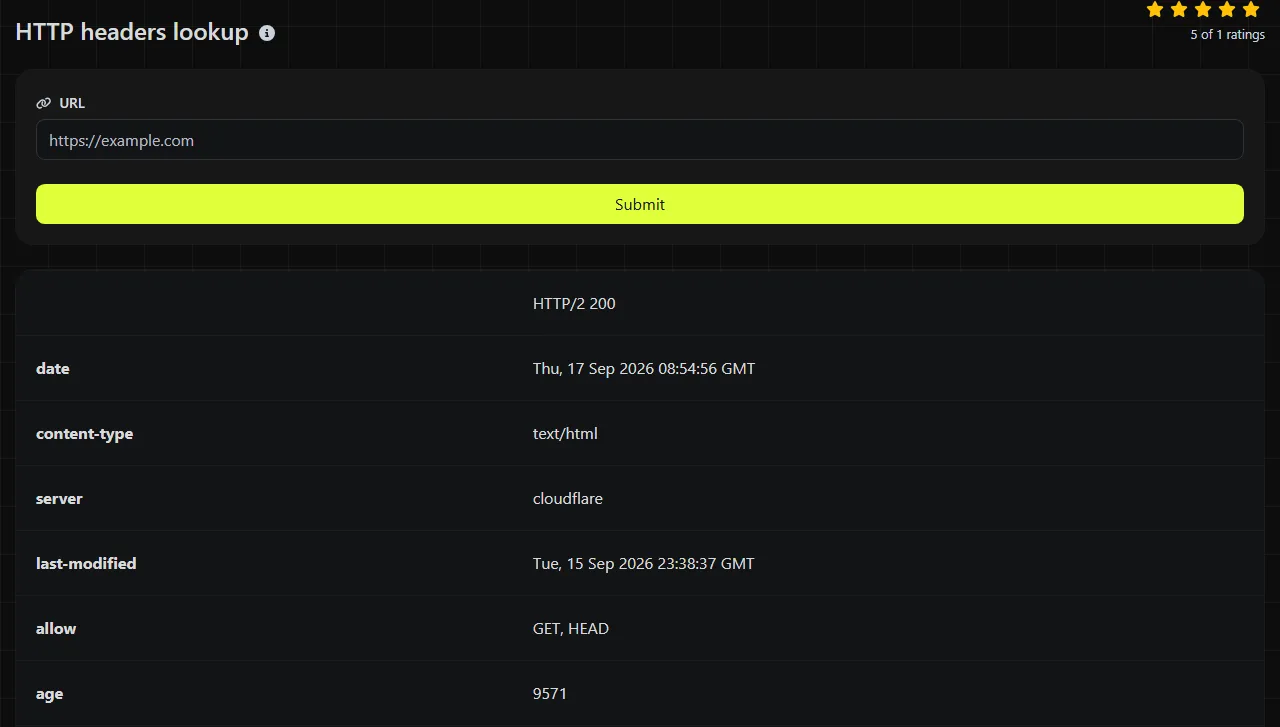
For example, a page response could contain Cache-Control: public, max-age=300 and Age: 126. Assuming no other constraints, that combination gives the response a five-minute freshness lifetime and indicates that approximately 174 seconds of freshness remain when it is received. These lines are illustrative because actual output depends entirely on the requested URL and the server's configuration.
When can header results narrow down a website problem?
Header results can narrow down problems involving redirects, stale content, incorrect file types, cookies, and browser security rules. They are most useful when the server completes the HTTP request but returns behavior you did not expect.
- A custom domain opens the wrong page. Check the exact HTTP and HTTPS URLs, with and without www. A returned Location field can expose a redirect to an old hostname, an unexpected path, or the wrong protocol.
- A new stylesheet or page version is still stale. Inspect Cache-Control, Age, ETag, and Last-Modified. A long freshness period or an older cached response can explain why a deployment is not visible through a CDN or proxy.
- A browser downloads a file instead of displaying it. Check Content-Type and Content-Disposition when present. An incorrect media type or an attachment disposition can produce behavior that differs from what the file extension suggests.
If a site does not resolve in DNS, no HTTP exchange can begin. This check does not report DNS records, mail routing, or domain registration details. Ping may help with basic host reachability, while Whois Lookup can provide registration information, but neither replaces a DNS record check.
Redirects, caches, and delayed changes
A correct header can appear wrong when different clients reach different servers or cached copies. Browsers, corporate proxies, CDNs, and hosting platforms may each cache a response for a period determined by configuration and response headers.
DNS changes create another delay. Resolvers may retain an earlier IP address until its DNS time to live expires, so the lookup server and your local browser can temporarily contact different origins. A server-side check also may receive a different response because it does not necessarily have your browser's cookies, session state, geographic route, or request history.
Compare the exact URL, including its scheme, hostname, path, and query parameters. Also compare the Age header and calculated remaining freshness at the time of each test. Repeating a request immediately may continue to reach the same cached object until its freshness period ends or the cache is purged through the relevant hosting or CDN controls.
What can this lookup not diagnose?
This lookup cannot diagnose every failure that occurs before or outside an HTTP response. A certificate validation failure, DNS lookup failure, blocked network route, or server timeout may prevent useful response headers from being returned at all.
It also does not inspect email headers or explain why a message was rejected. Email delivery normally depends on SMTP responses and DNS records such as MX, SPF, DKIM, and DMARC rather than website response headers.
The request is made on the server. The URL you enter travels to the server over HTTPS and is not stored. The destination website still receives the request as part of the normal HTTP exchange, so do not place passwords, private API keys, reset tokens, or other secrets in the URL.
Characters not allowed directly in a URI, including spaces and non-ASCII characters, require percent-encoding when serialized as a URI, while internationalized domain names use separate IDN handling and may appear in their ASCII-compatible form.
Common questions about HTTP header checks
Why is the Content-Length header missing?
Content-Length may be absent when the response size is not known before transmission, when streaming is used, or when the protocol frames the body without that field.
Can the bare domain and www domain return different headers?
Yes. example.com and www.example.com are different hostnames and can use different servers, redirect rules, cookies, caching policies, and security headers. Check both when diagnosing a domain migration or canonical-host problem.
What do X-Cache, CF-Cache-Status, or similar fields mean?
These are provider-specific headers commonly used to report cache behavior, such as a hit, miss, bypass, or expired object. Their exact values are not standardized, so interpret them using the documentation for the CDN or proxy that added them.
Will an authenticated API return useful headers?
It may return headers, but a typical GET without the required credentials can receive an authentication error rather than the protected resource.
Should I remove query parameters before checking a URL?
Remove them only if you want to test the base resource. Query parameters can select content, trigger redirects, or form part of a cache key, so preserving them is necessary when reproducing a specific problem. Before sharing results, remove sensitive parameter values and record the exact sanitized URL you checked.
Popular tools
Create a WhatsApp chat link from a phone number, with an optional prefilled message.