HTML entity converter
Encode or decode HTML entities for any given input.
HTML entity converter is a free tool that encodes characters as HTML entities or decodes entity references into readable characters.
When should ampersands and angle brackets be escaped?
Ampersands and angle brackets should be escaped when a browser could interpret them as the start of an entity or an HTML tag rather than as visible text. HTML character references represent characters with a named character reference such as & or a numeric character reference such as &.
For example, the plain text input is Fish & Chips. Its entity-encoded form is Fish & Chips. Decoding reverses that representation.
Escaping is commonly needed when displaying code samples, mathematical comparisons, company names containing ampersands, or user-supplied text inside HTML. Quotation marks may also need encoding inside HTML attributes, depending on which quotation mark surrounds the attribute value.
Modern HTML supports Unicode, so accented letters, non-Latin scripts, and emoji can usually remain as characters when the document uses UTF-8. Numeric entities remain useful when a character must be represented without placing it directly in the source.
Choosing the encoding that matches the data
HTML entities belong to HTML source and should not be used as a general-purpose encoding for every text-based channel. Several formats can make data look encoded, but they use different rules and require different decoders.
- HTML pages commonly use named or numeric character references, including &, <, and ©.
- Query strings commonly use percent encoding. An ampersand may separate parameters, while spaces may appear as %20 or as a plus sign in application/x-www-form-urlencoded data. A URL decoder is the appropriate choice for that format.
- Data URLs may contain percent-encoded data or Base64 data after the comma.
- Email may use MIME transfer encodings such as Base64 or quoted-printable.
- JSON payloads use JSON escapes such as \n, \" and Unicode escape sequences. HTML entities do not have special meaning to a JSON parser.
- Internationalized domain names can use Punycode labels beginning with xn--. An IDN Punycode converter handles those labels.
A value copied from a URL, email header, API response, or domain name may not contain HTML entities at all.
A short conversion walkthrough
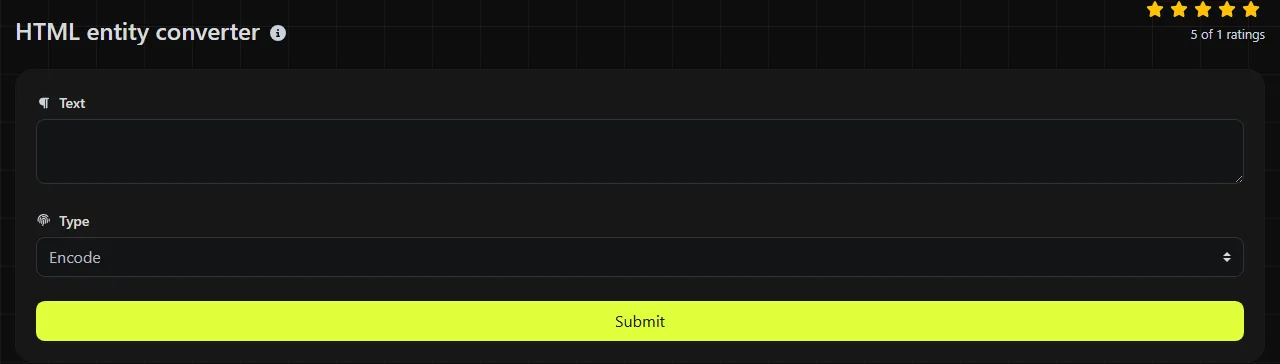
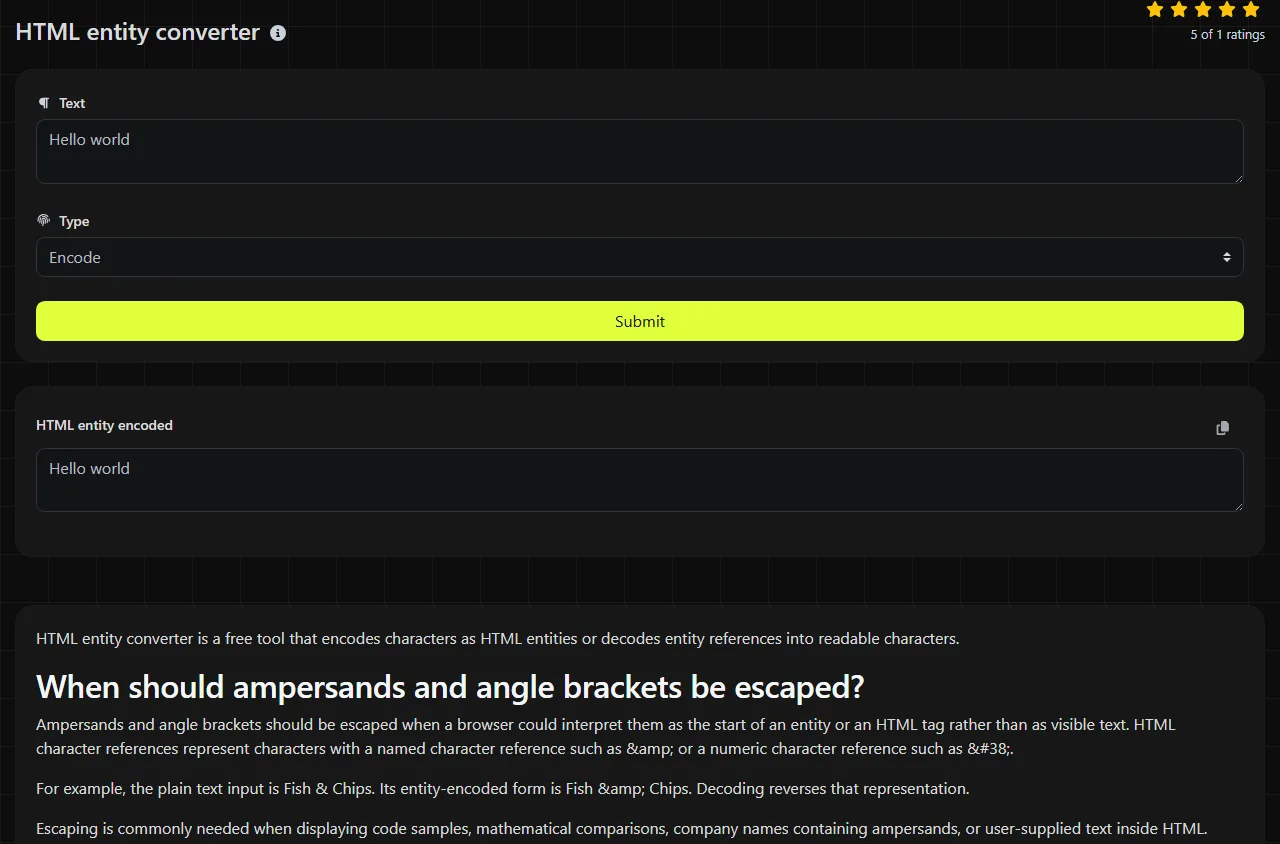
Use Encode when ordinary characters need an HTML entity representation, and use Decode when the input already contains entity references. The corresponding results appear in HTML entity encoded and HTML entity decoded.
A decoding example uses the literal input Price < $25. The decoded result is Price < $25. Numbers and dollar signs remain unchanged because they are not entity references in that input.
The work is performed on the server. Your input travels to the server over HTTPS and is not stored.
For decoding, the server-side implementation uses PHP's html_entity_decode function.
Why is an entity reference still unchanged after decoding?
An entity reference may remain unchanged because its syntax is incomplete, its name is invalid, or the data uses a different representation, such as percent encoding or Base64. Check the original value for multiple layers of HTML character-reference encoding before repeatedly decoding it.
- Missing semicolon can make a reference ambiguous or invalid. Prefer & rather than & without the final semicolon.
- Double encoding can leave another encoded layer after one decoding pass. For example, &amp; may decode once to & and require another deliberate decode to become an ampersand.
- Wrong format is common when the input includes percent escapes, Base64 characters, JSON escapes, or Punycode.
Gibberish can also indicate a character-encoding mismatch, such as interpreting UTF-8 bytes with a different character set. Entity decoding alone does not repair damaged bytes or determine the original character encoding.
Can HTML entities keep information secret?
No, character-reference encoding is readily reversible and provides no secrecy. Entity encoding exists to represent characters safely in HTML source, which is different from encryption.
Encoding also does not automatically make untrusted content safe in every context. HTML text, attribute values, URLs, CSS, and JavaScript each have different escaping rules. Software that inserts user-controlled content into a page should apply context-aware escaping at output time and should not rely on a manual conversion as its only security control.
Frequently asked questions
Can numeric HTML entities use hexadecimal numbers?
Yes. Decimal references use a form such as ©, while hexadecimal references use a form such as ©. The x identifies the number as hexadecimal, and the terminating semicolon should be included.
What happens if the decoded character is an emoji?
A numeric character reference can represent an emoji by its Unicode code point. The decoded character still requires a Unicode-capable font and rendering system, so an unsupported emoji may appear as an empty box or replacement symbol.
Can I omit the semicolon at the end of an entity?
Browsers tolerate some missing semicolons in limited HTML parsing situations, but the result can depend on the characters that follow. Include the semicolon to avoid ambiguity, especially in attribute values and generated markup.
Do line breaks have HTML entities?
Numeric references can represent carriage return and line feed characters, but a line break in source does not necessarily create a visible break on an HTML page. Normal HTML whitespace handling may collapse it, so visible layout usually requires an appropriate HTML element or CSS rule.
Can I decode entities before placing text in an HTML attribute?
You can, but the decoded result may contain quotation marks, ampersands, or angle brackets that affect the attribute's markup. Escape the final value for the specific attribute context before inserting it into HTML.
Paste-ready checks
Inspect how an HTML parser or browser renders the result rather than judging it only as plain text. Confirm that intended tags remain markup, visible angle brackets remain text, ampersands are not starting accidental references, and no extra decoding layer has exposed unsafe characters.
Popular tools
Create a WhatsApp chat link from a phone number, with an optional prefilled message.