Bcrypt generator
Generate a bcrypt password hash for any string input.
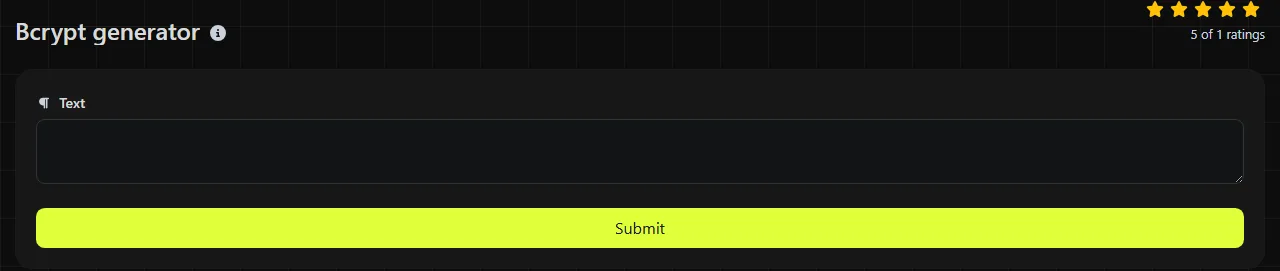
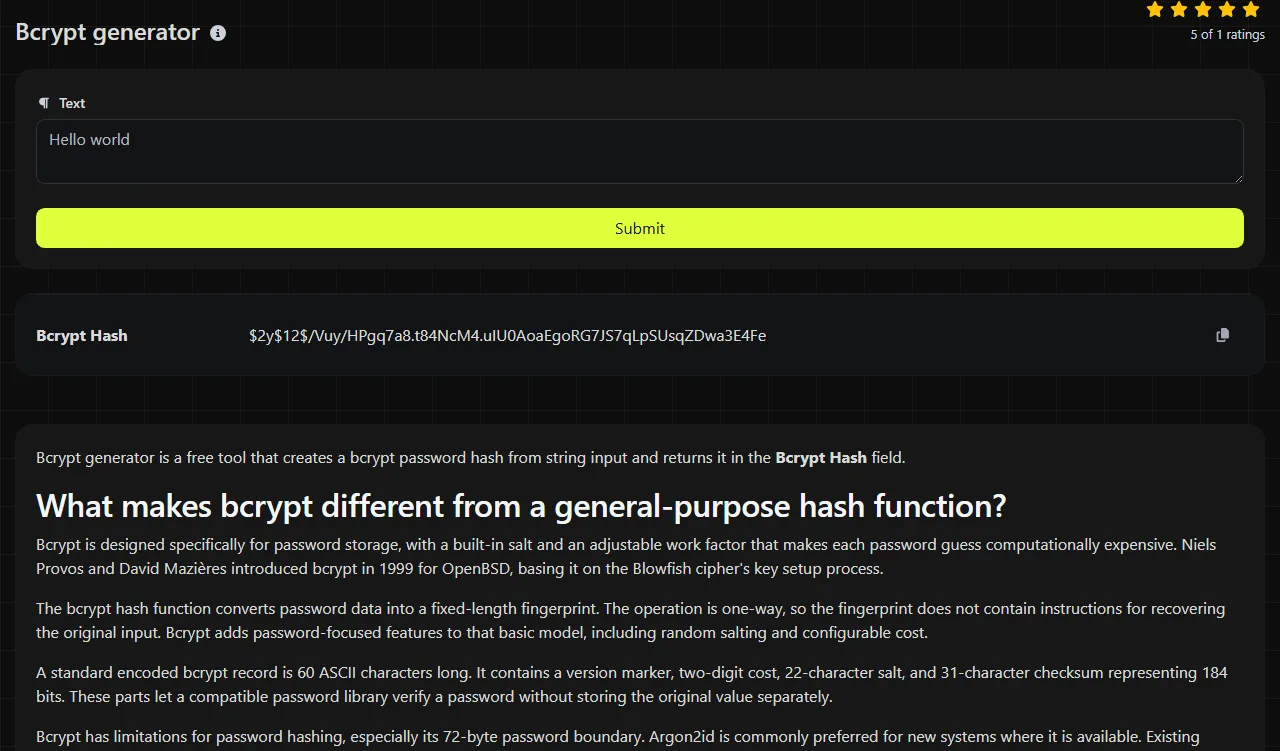
Bcrypt generator is a free tool that creates a bcrypt password hash from string input and returns it in the Bcrypt Hash field.
What makes bcrypt different from a general-purpose hash function?
Bcrypt is designed specifically for password storage, with a built-in salt and an adjustable work factor that makes each password guess computationally expensive. Niels Provos and David Mazières introduced bcrypt in 1999 for OpenBSD, basing it on the Blowfish cipher's key setup process.
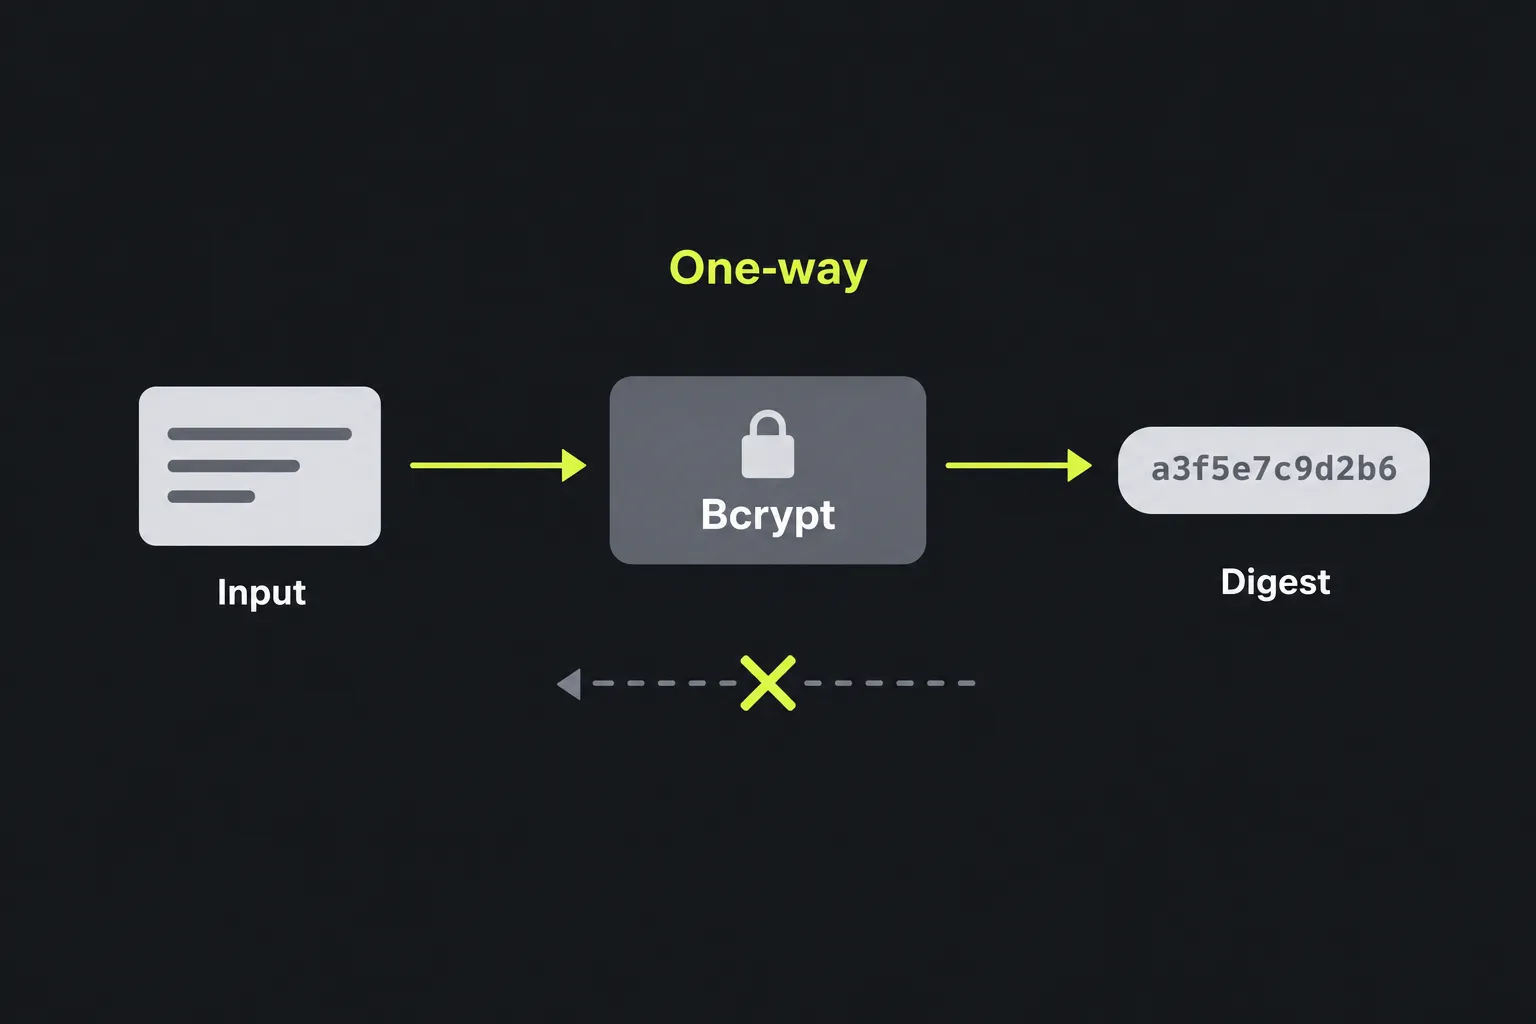
The bcrypt hash function converts password data into a fixed-length fingerprint. The operation is one-way, so the fingerprint does not contain instructions for recovering the original input. Bcrypt adds password-focused features to that basic model, including random salting and configurable cost.
A standard encoded bcrypt record is 60 ASCII characters long. It contains a version marker, two-digit cost, 22-character salt, and 31-character checksum representing 184 bits. These parts let a compatible password library verify a password without storing the original value separately.
Bcrypt has limitations for password hashing, especially its 72-byte password boundary. Argon2id is commonly preferred for new systems where it is available. Existing bcrypt deployments can remain acceptable when they use a suitable cost and sound password-handling practices.
How do I generate a bcrypt value for an application?
Provide the exact password text that the application will later verify, run the generator, and copy the returned Bcrypt Hash as one complete value. Do not remove the prefix, cost, salt, or checksum.
The tool calls PHP's password_hash function on the server. The password text entered in Bcrypt generator travels to the server over HTTPS and is not stored. Because the work is server-side, avoid submitting a real production password if your security policy prohibits sending credentials to third-party services.
For example, an input such as Cedar Cabin 47! produces a 60-character bcrypt record. Running the same input again will normally produce a different record because password hashing generates a new random salt. Both records can still verify the same password.
In PHP, an application should check a saved record with password_verify. It should not generate a fresh bcrypt record and compare the two strings directly, since the newly generated salt will make the strings different.
Password verification and attack limits
A bcrypt hash cannot be decrypted or directly reversed because bcrypt is a one-way operation, not encryption. Verification works by taking a password candidate, reading the salt and cost from the stored record, repeating the bcrypt calculation, and comparing the result.
An attacker can still guess passwords. Common passwords and short patterns may be found through dictionary or brute-force attacks, even when bcrypt is implemented correctly. The cost slows each guess, while the unique salt prevents attackers from efficiently reusing one precomputed table across many accounts.
The encoded bcrypt cost parameter is the base-2 logarithm of the work factor. Raising it by one approximately doubles the required computation. Application owners should choose a cost their authentication systems can handle, monitor login performance, and increase it over time when practical. This generator creates a hash, but it does not determine the right operational cost for a particular server workload.
Which tasks are a good fit for bcrypt?
Use bcrypt for password records and compatibility with systems that already support the bcrypt format. It is a poor choice for deterministic checksums, file integrity labels, content deduplication, or cache keys because its random salt causes the same input to produce different encoded results.
- Appropriate use includes storing a password verifier in an application database.
- Legacy compatibility includes generating records for an established bcrypt-based authentication system.
- Not appropriate includes finding duplicate files by comparing hashes.
- Not appropriate includes signing messages or proving that a file came from a particular sender.
For a deterministic integrity fingerprint, a general-purpose cryptographic hash such as the SHA-3/384 generator or SHA-3/512 generator fits better. Those algorithms are not substitutes for bcrypt when storing human-chosen passwords because they are intentionally fast.
Input boundaries and exact-byte behavior
Bcrypt processes bytes, so spaces, punctuation, capitalization, and encoding all affect the result. River7, river7, and River7 are different inputs. Numbers entered in Bcrypt generator's text field are handled as their character representation rather than as mathematical values.
For bcrypt input, accented letters, emoji, and characters in non-Latin scripts commonly occupy multiple bytes in UTF-8. Bcrypt has an effective input boundary of 72 bytes in common implementations, which is not necessarily 72 visible characters. Some libraries truncate longer input while others reject it, so an application should enforce a documented limit and use the same encoding during account creation and login.
An empty input can have a valid bcrypt representation, but that does not make an empty password safe. Hidden leading or trailing spaces can also cause login failures if one part of a system trims them and another preserves them.
Common questions about bcrypt
Should an application add a pepper as well as the bcrypt salt?
A pepper can add protection when it is a secret stored outside the password database, such as in a secrets manager. It complicates rotation and recovery, so it requires a documented design rather than simply appending a hard-coded value in application source code.
Can bcrypt hashes move between PHP and another programming language?
Usually, if both libraries support the same bcrypt version marker and encoded record format. Test migration with disposable passwords first, since older libraries may recognize only certain prefixes or apply different handling to unusual input.
Is bcrypt suitable for API keys or randomly generated tokens?
It can protect token values, but bcrypt's 72-byte boundary and relatively large verification cost may be unnecessary for high-entropy tokens. A keyed hash such as HMAC is often easier to operate for server-generated tokens, provided the secret key is stored separately and protected.
Can a bcrypt record reveal that two users chose the same password?
Normally no. Independently generated salts cause the stored records to differ even when the underlying passwords match. An observer can still see the bcrypt version and cost because those values are part of the encoded record.
Final checks
- Store the entire returned record without changing its characters or spacing.
- Confirm that the database column preserves all 60 characters.
- Use a bcrypt-aware verification function rather than direct string comparison.
- Set and document a password length policy in bytes as well as characters.
- Keep hashes protected as sensitive authentication data, even though they cannot be decrypted.
Popular tools
Create a WhatsApp chat link from a phone number, with an optional prefilled message.